
Description
Know what is happening on your WordPress site — without jumping between tools.
Broken links. Missing image descriptions. Database bloat. Unexpected admin activity. Problems are easier to fix when you can actually see them. Aegra Site Monitor brings practical WordPress diagnostics, traffic insights and everyday site checks into one organised dashboard.
Start with ten free modules. Check what’s working, spot what needs attention, and explore the details without digging through separate screens or plugins. Need deeper investigation? Aegra Pro adds historical tracking, advanced diagnostics, scheduled checks and alerts.
What Can Aegra Help You Find?
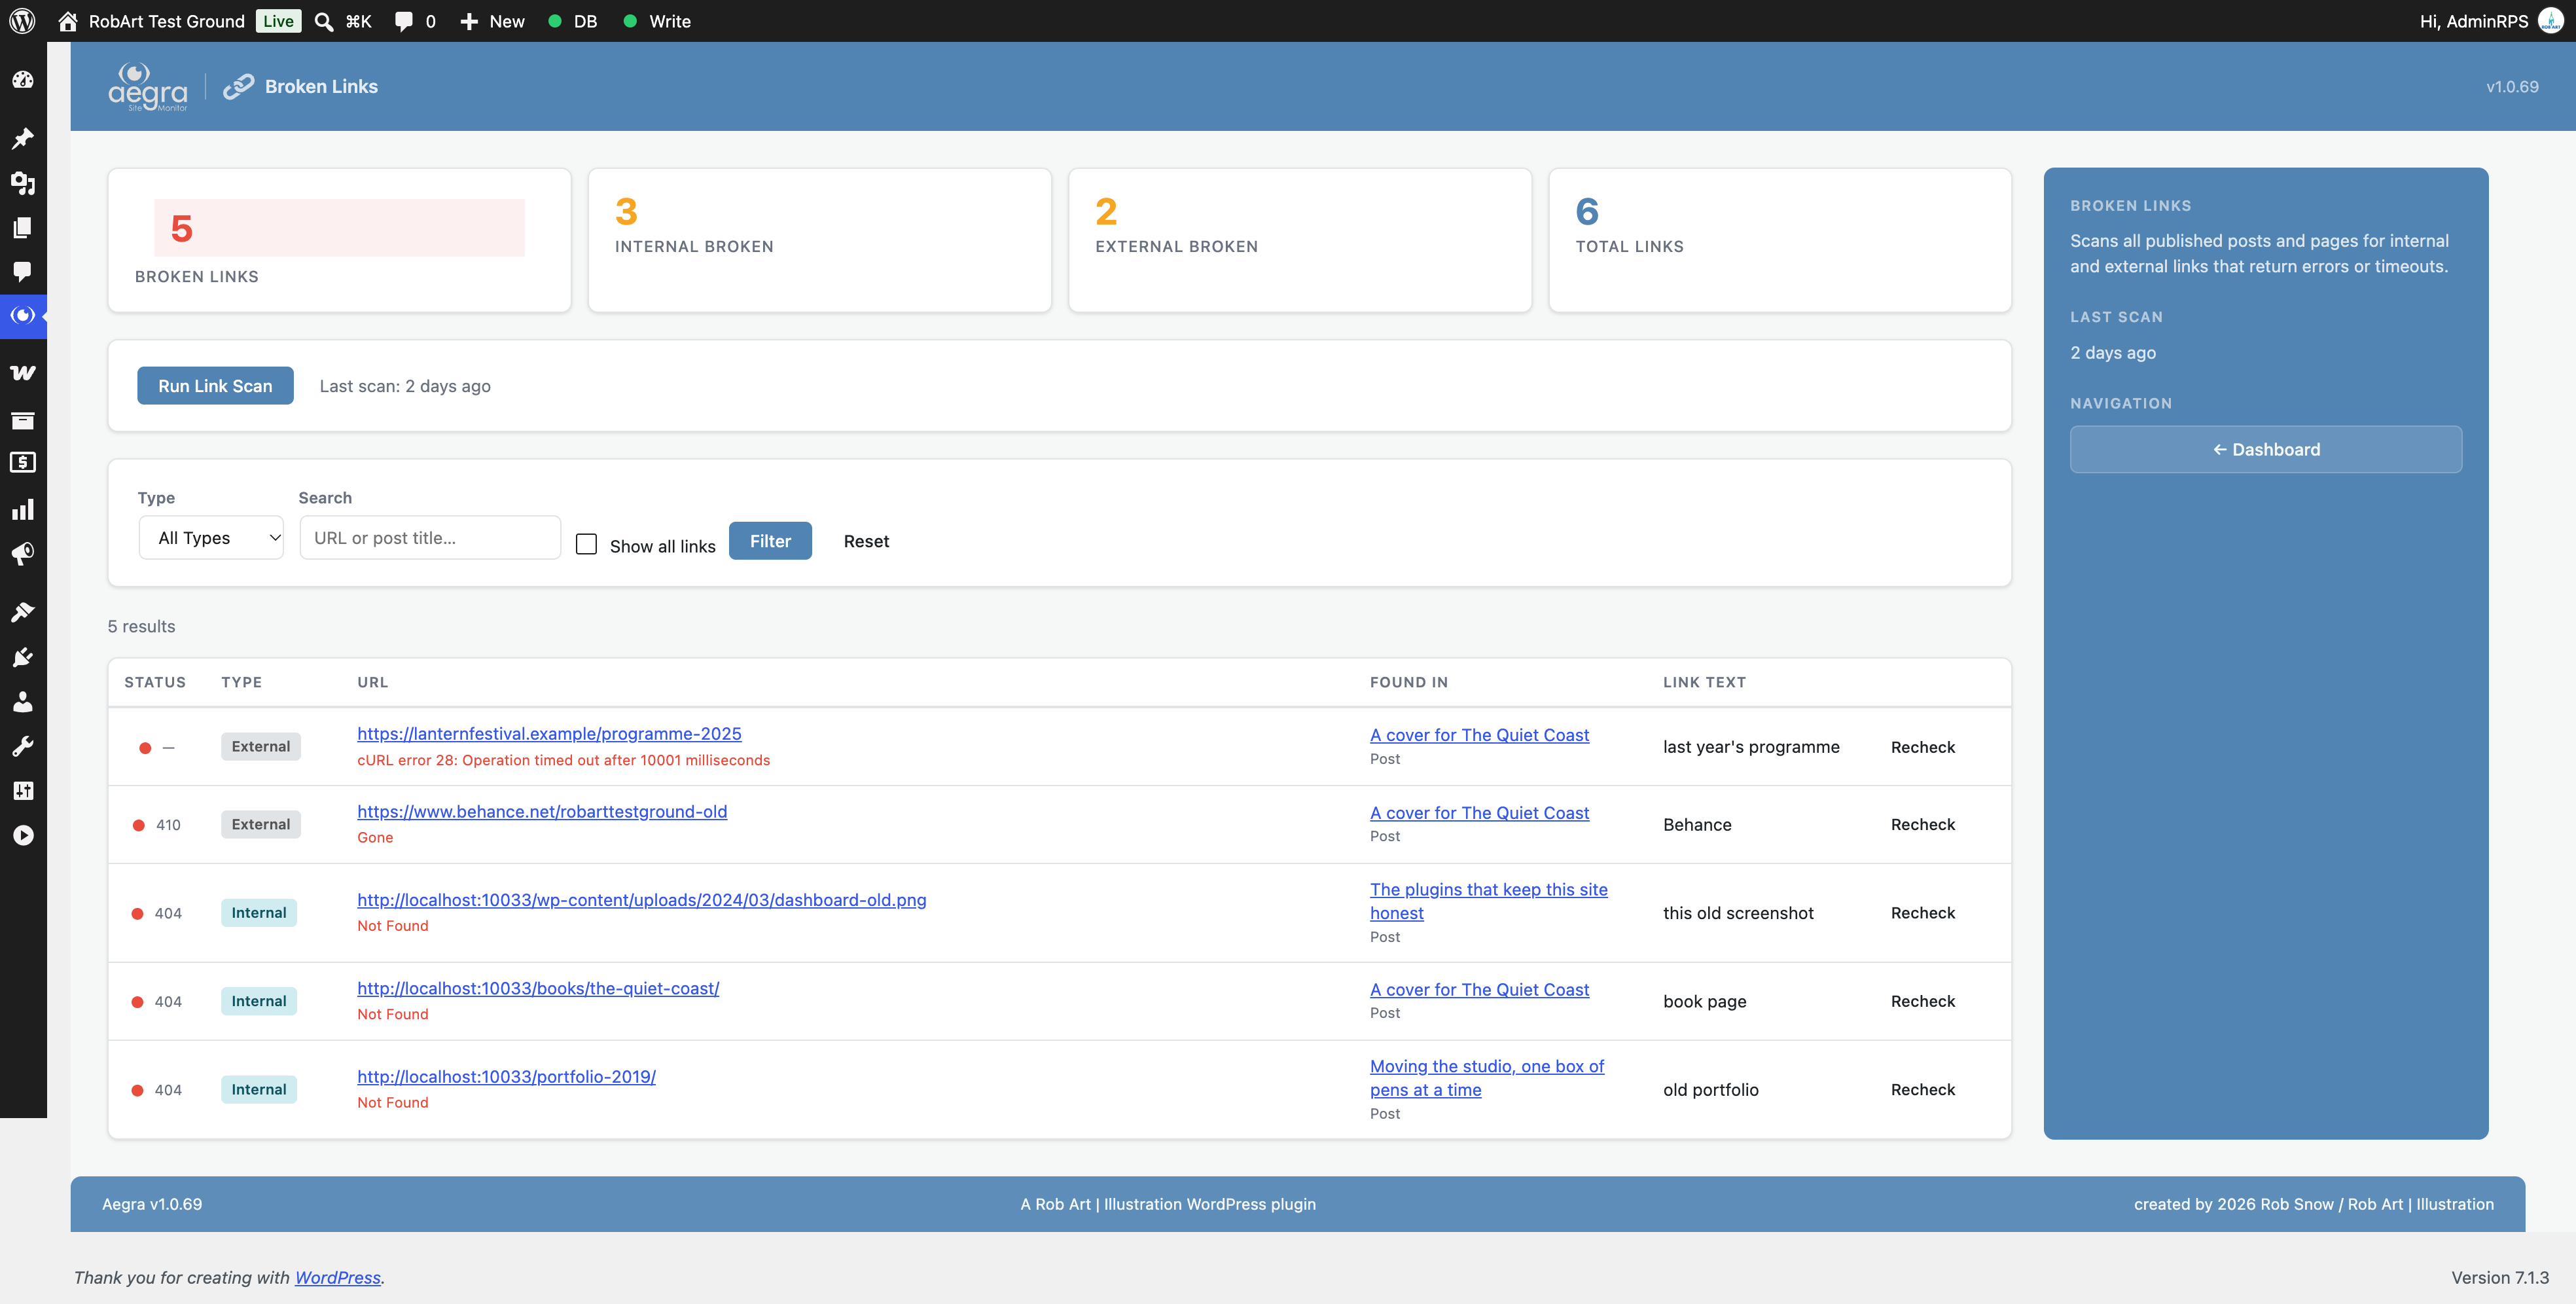
- Broken links: Find links that no longer work, then recheck them after making changes.
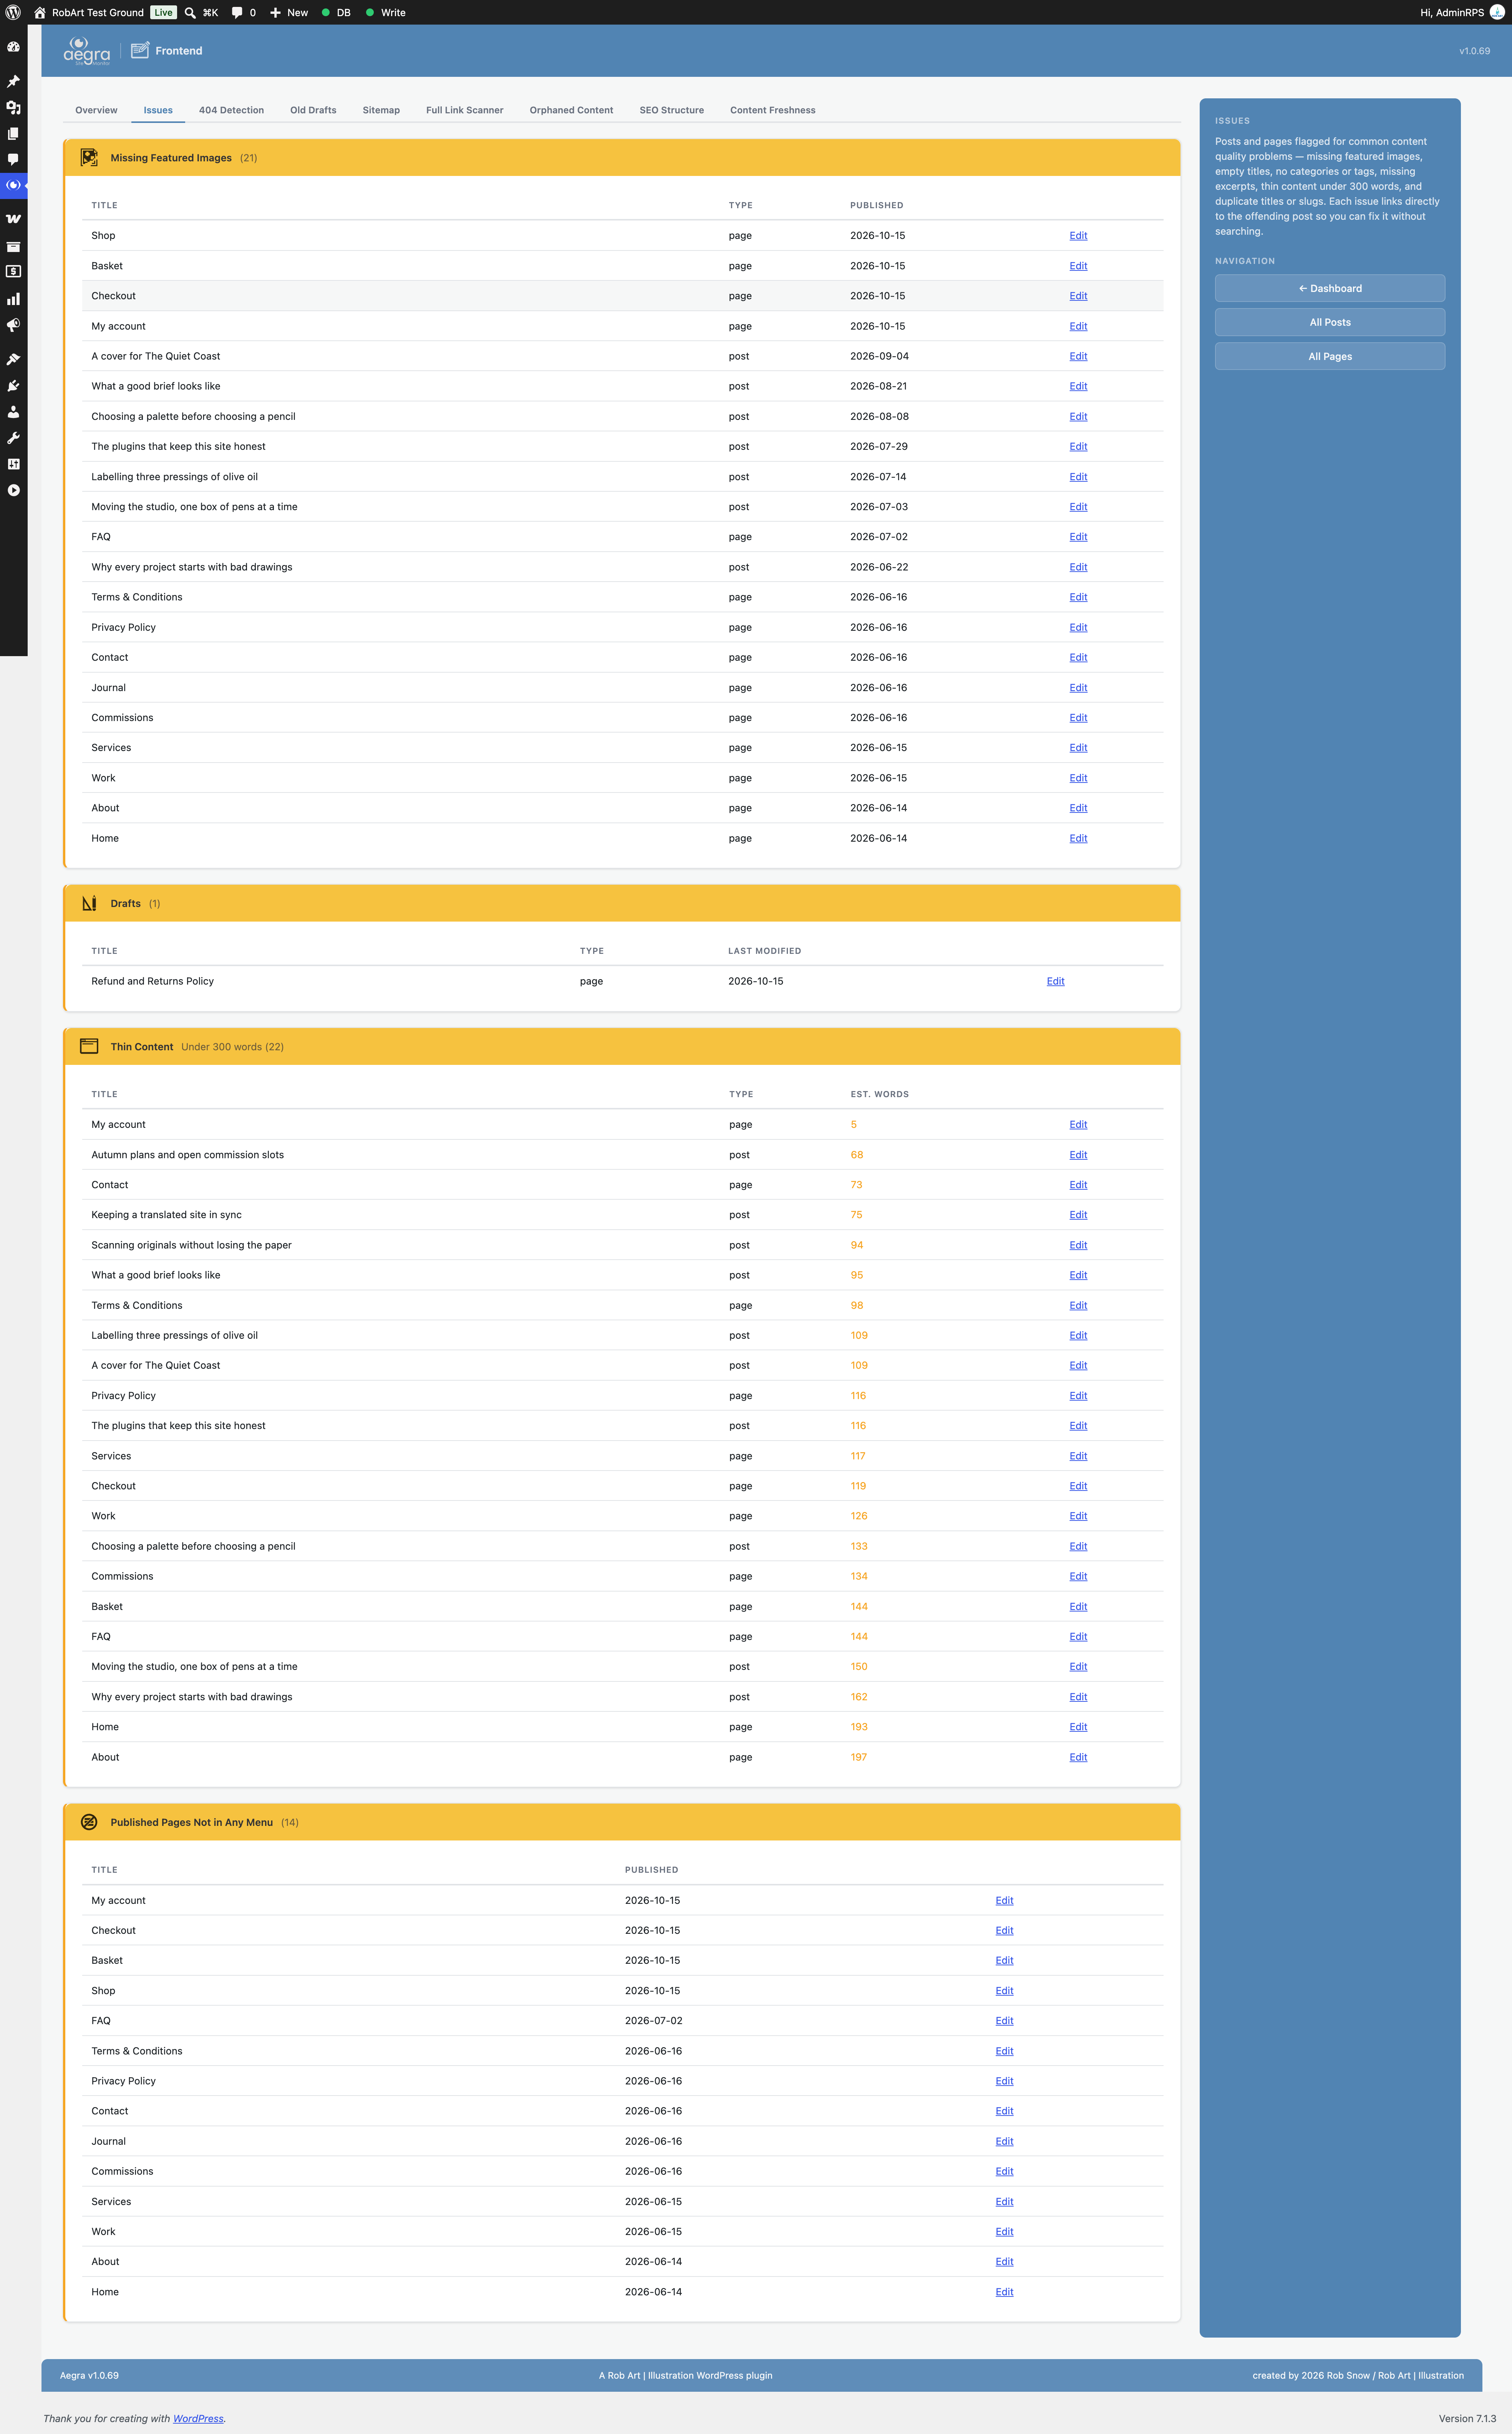
- Content gaps: Spot drafts, missing images and media items without alt text.
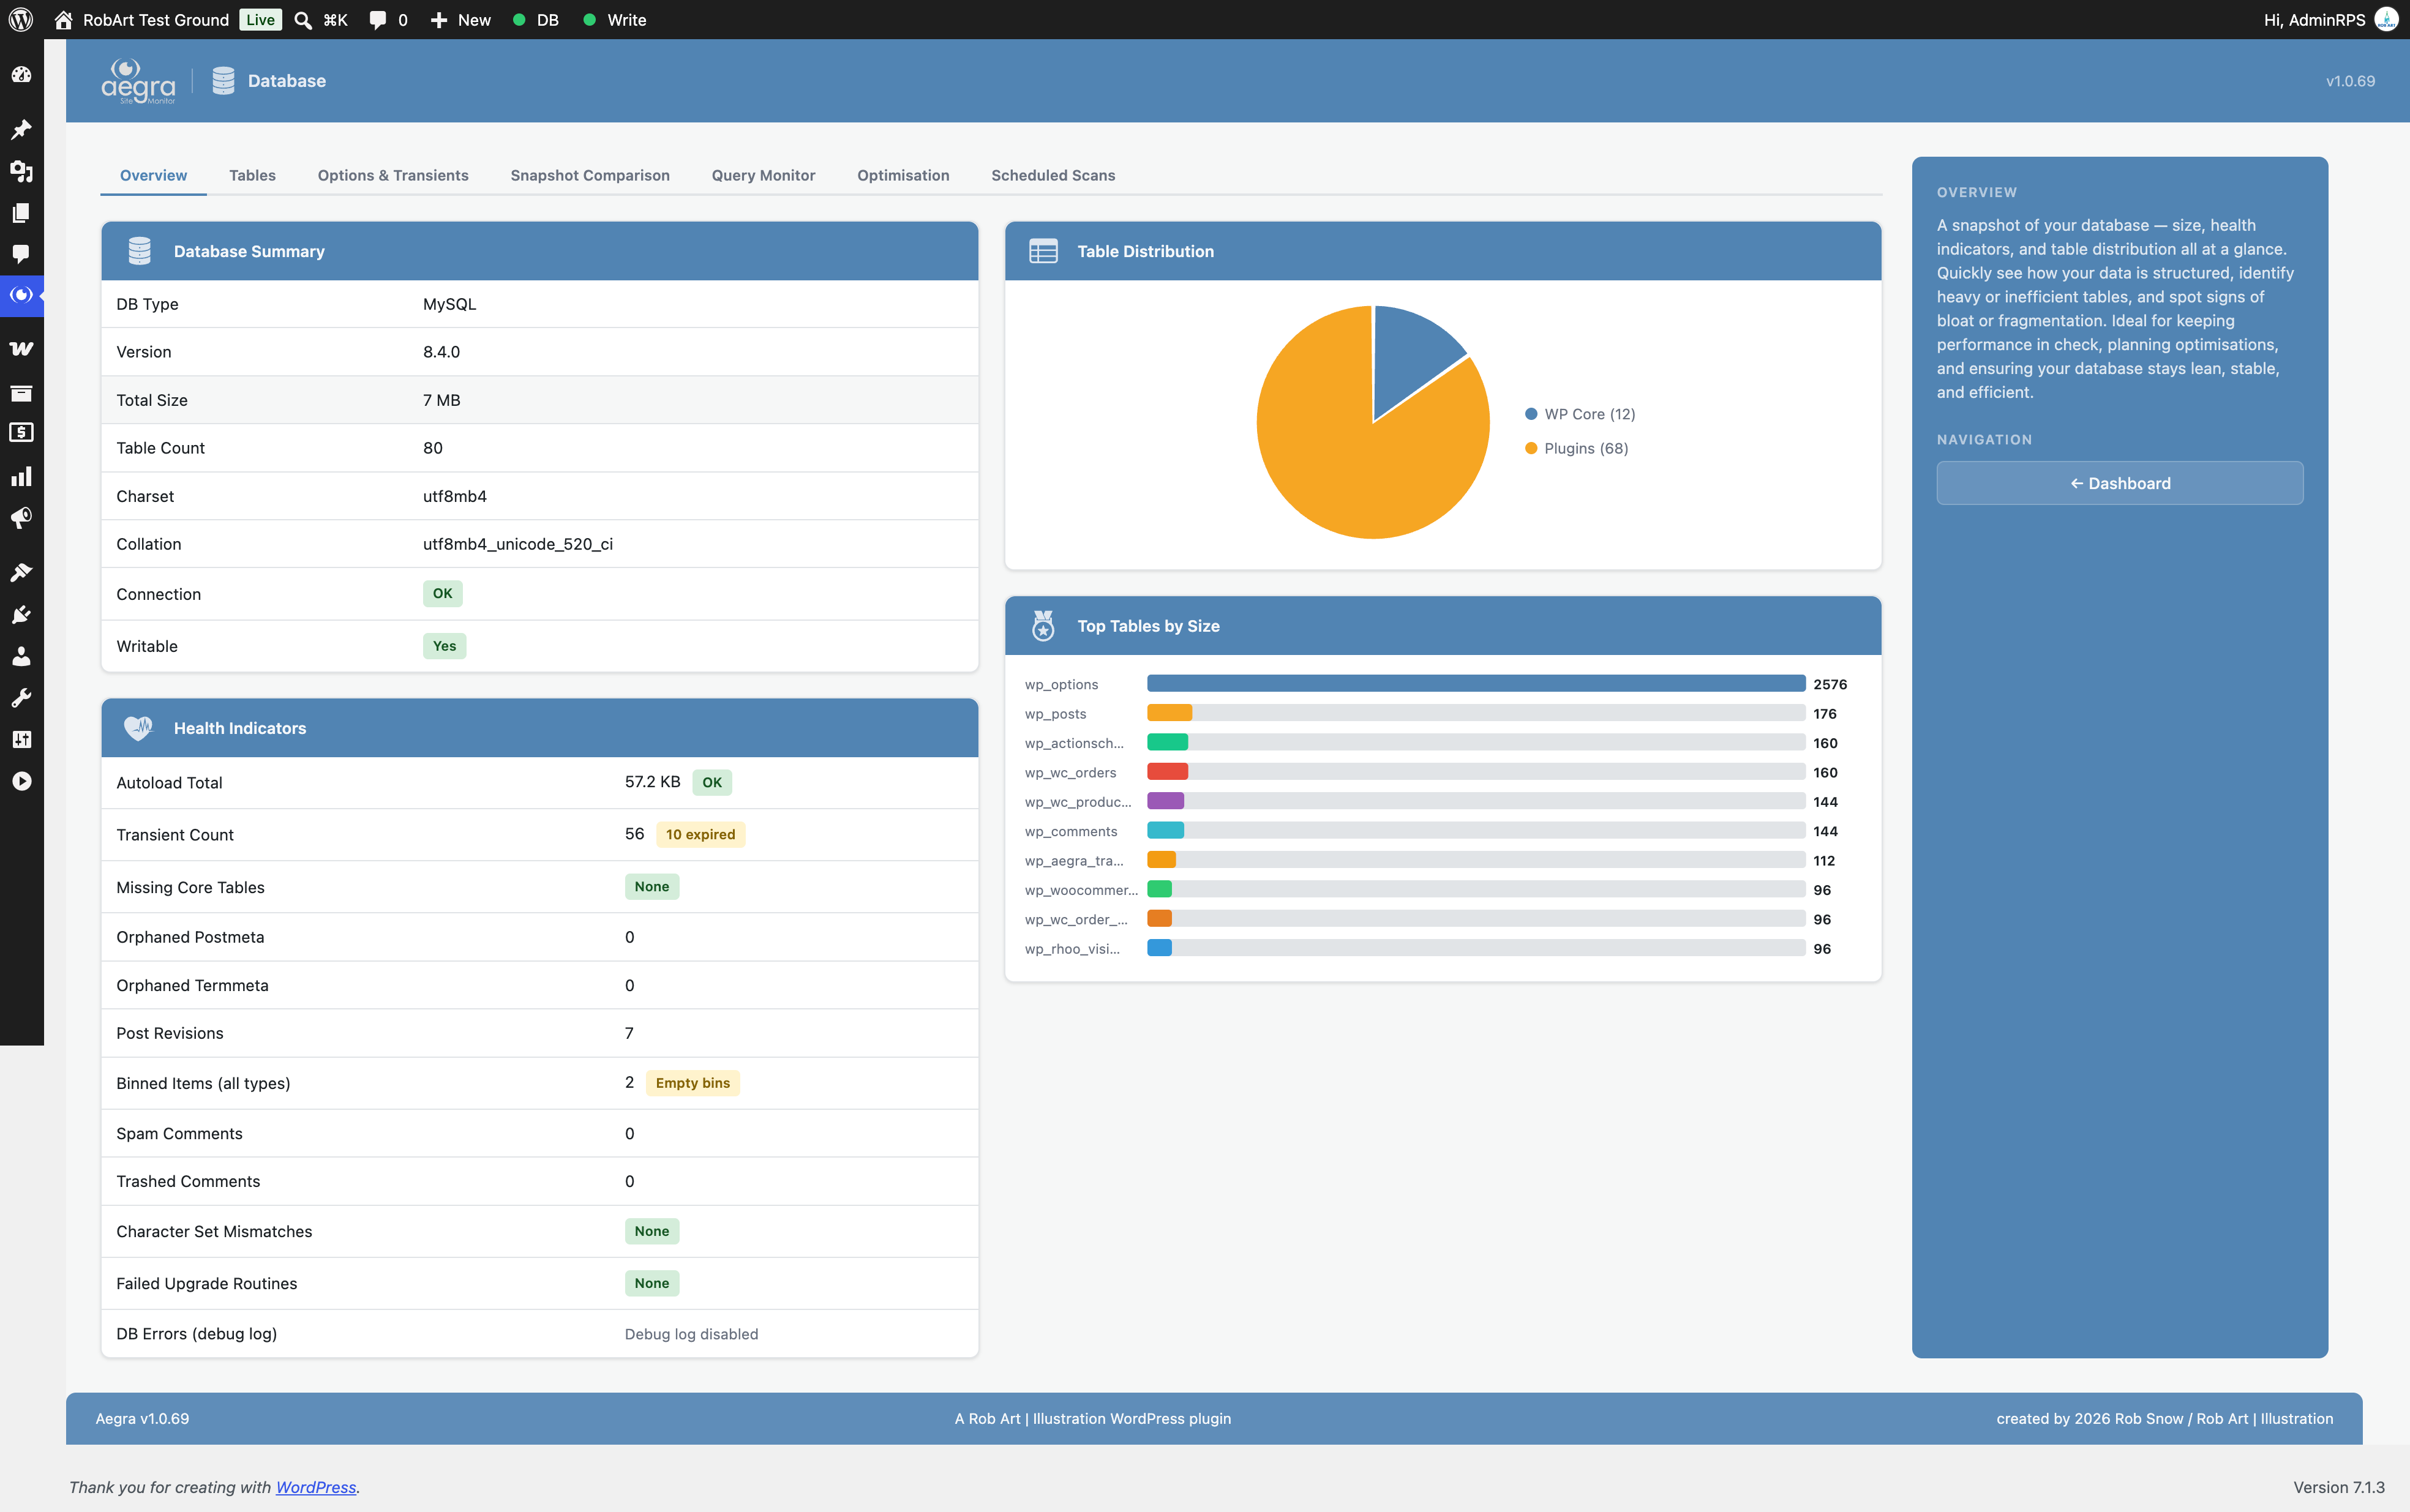
- Database trouble spots: Review table sizes, autoloaded data and transients before small issues become harder to manage.
- Site activity: See logins, admin sessions and plugin changes in one place.
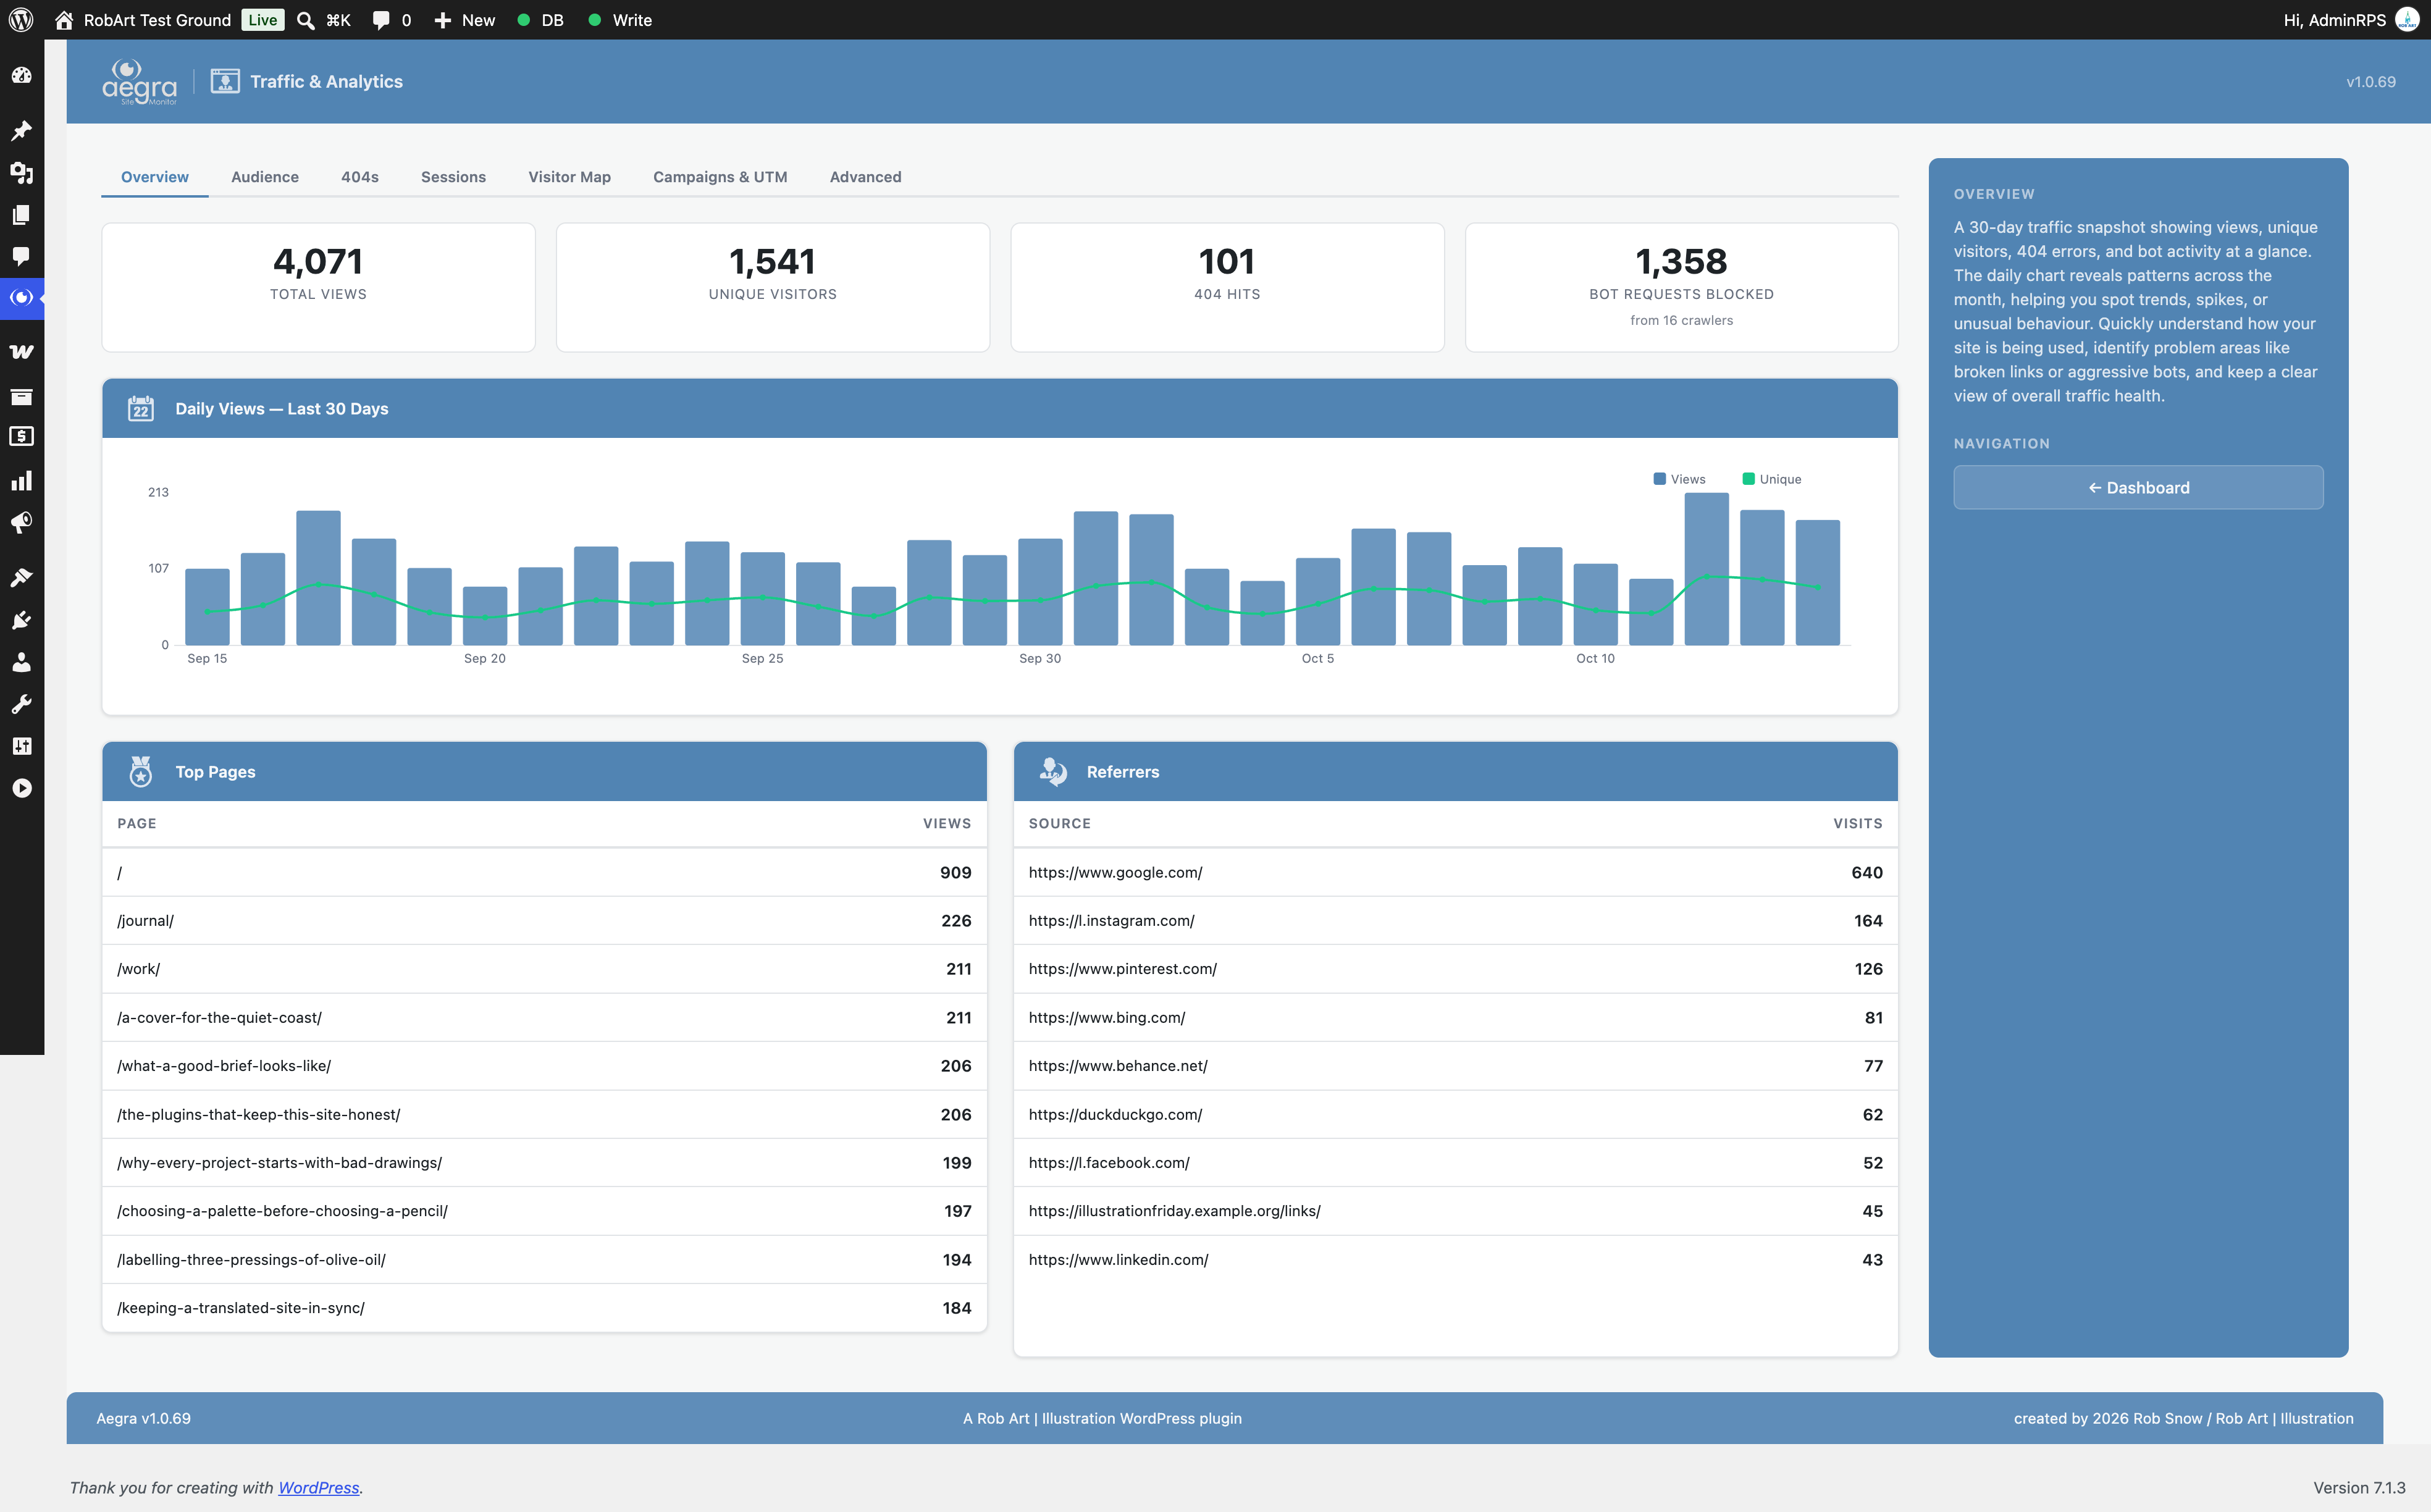
- Traffic patterns: Understand views, referrers, visitor devices and countries.
- Technical essentials: Check your WordPress, PHP, server, plugins and themes without hunting for details.
Free Features — Ten Modules, One Dashboard
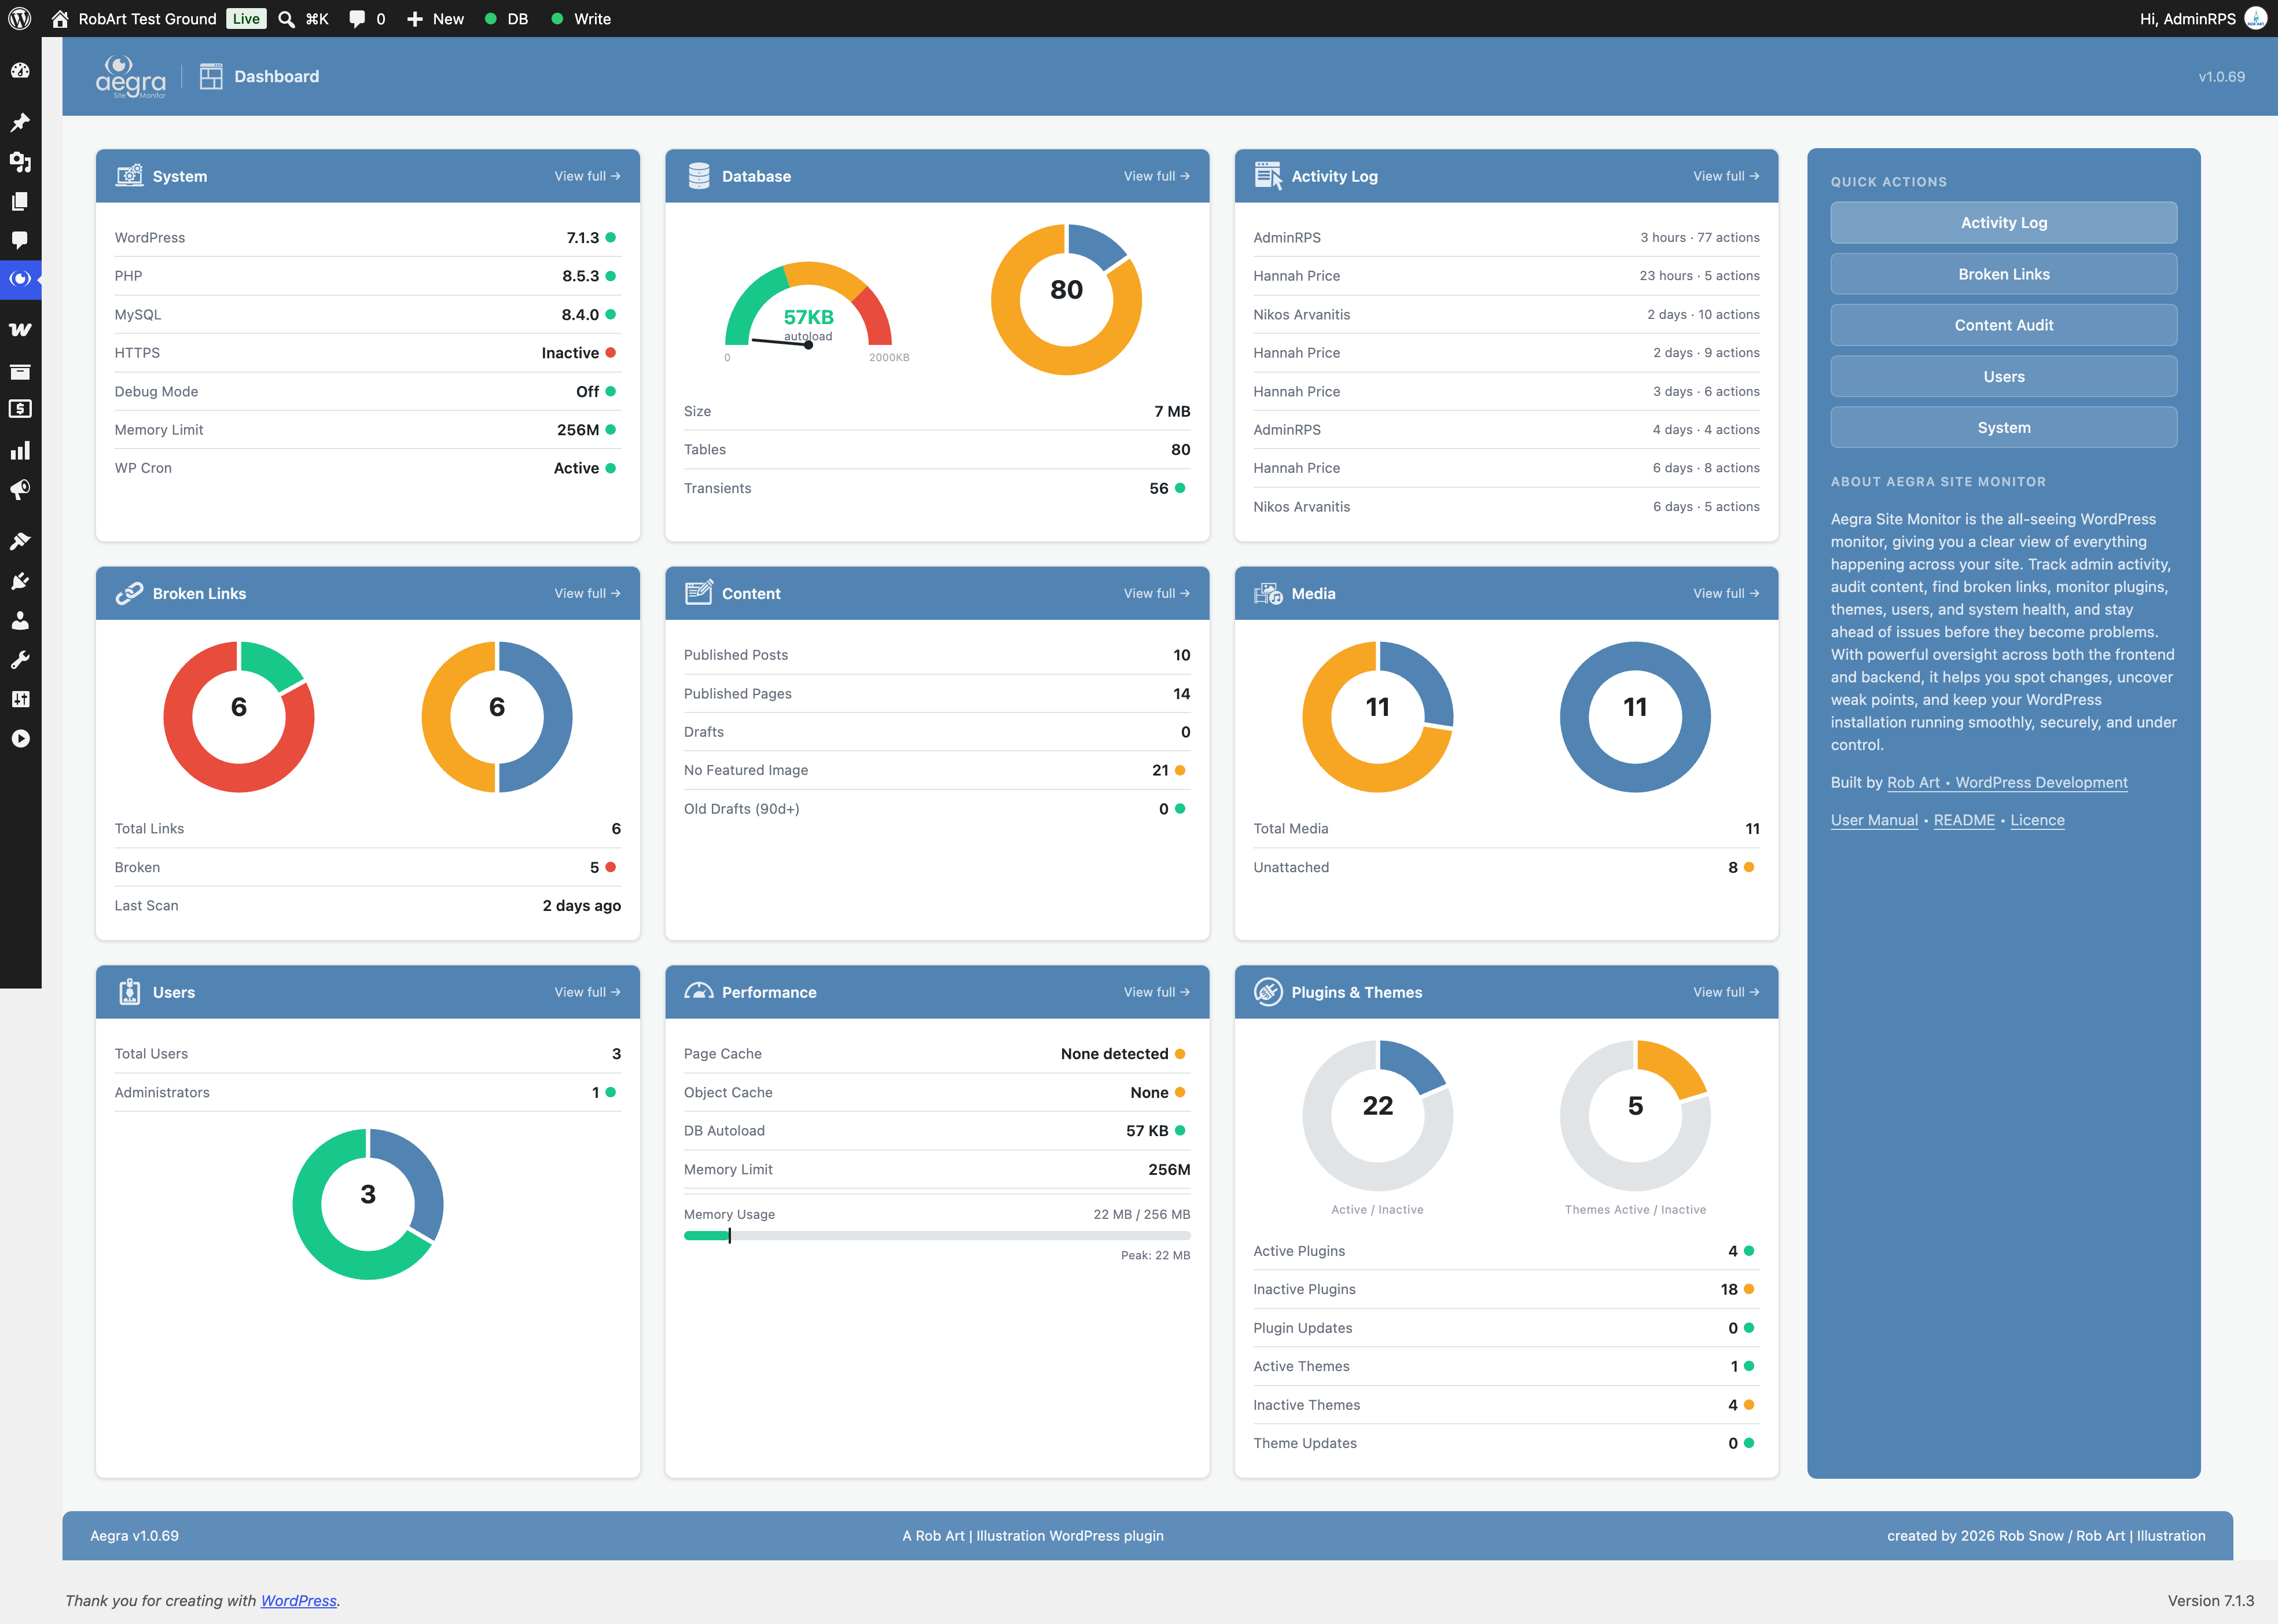
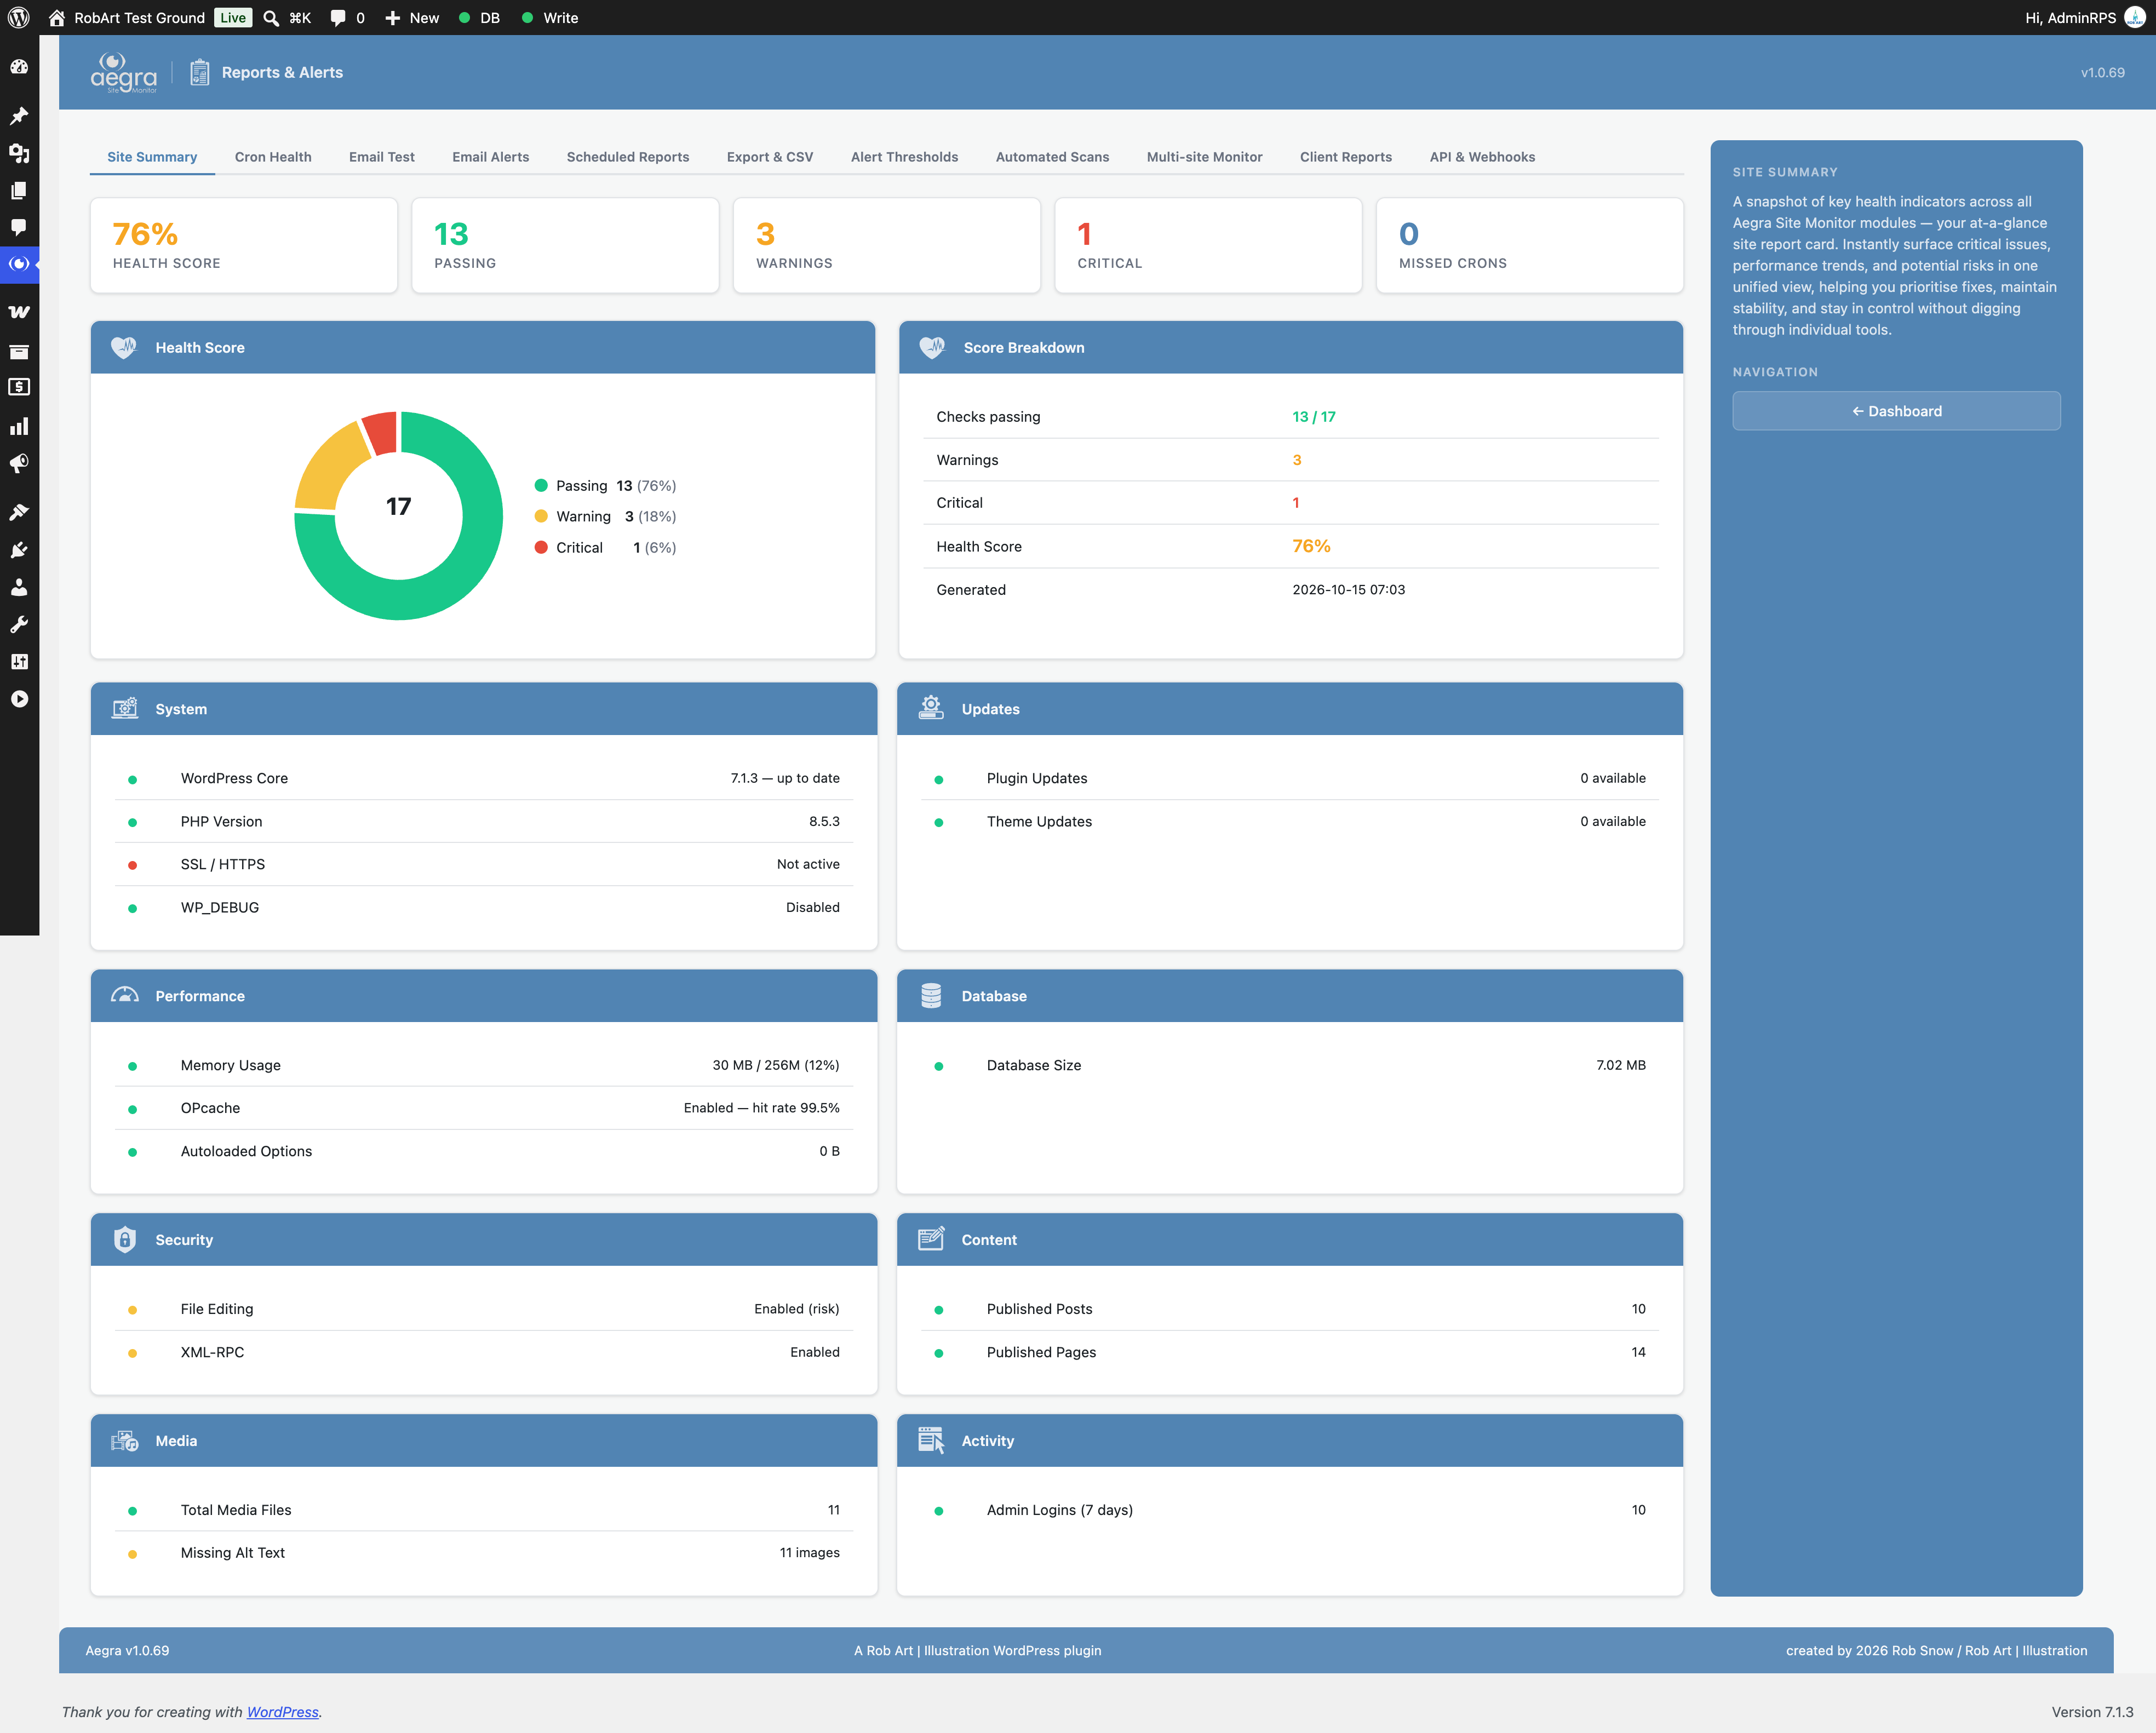
- Dashboard: An at-a-glance overview with live stats and module summaries.
- Activity Log: Review admin sessions, logins and plugin changes.
- Broken Links: Run manual scans, inspect results and recheck links.
- Content: Audit post counts, drafts and missing images.
- Database: Examine table sizes, autoloaded data and transients.
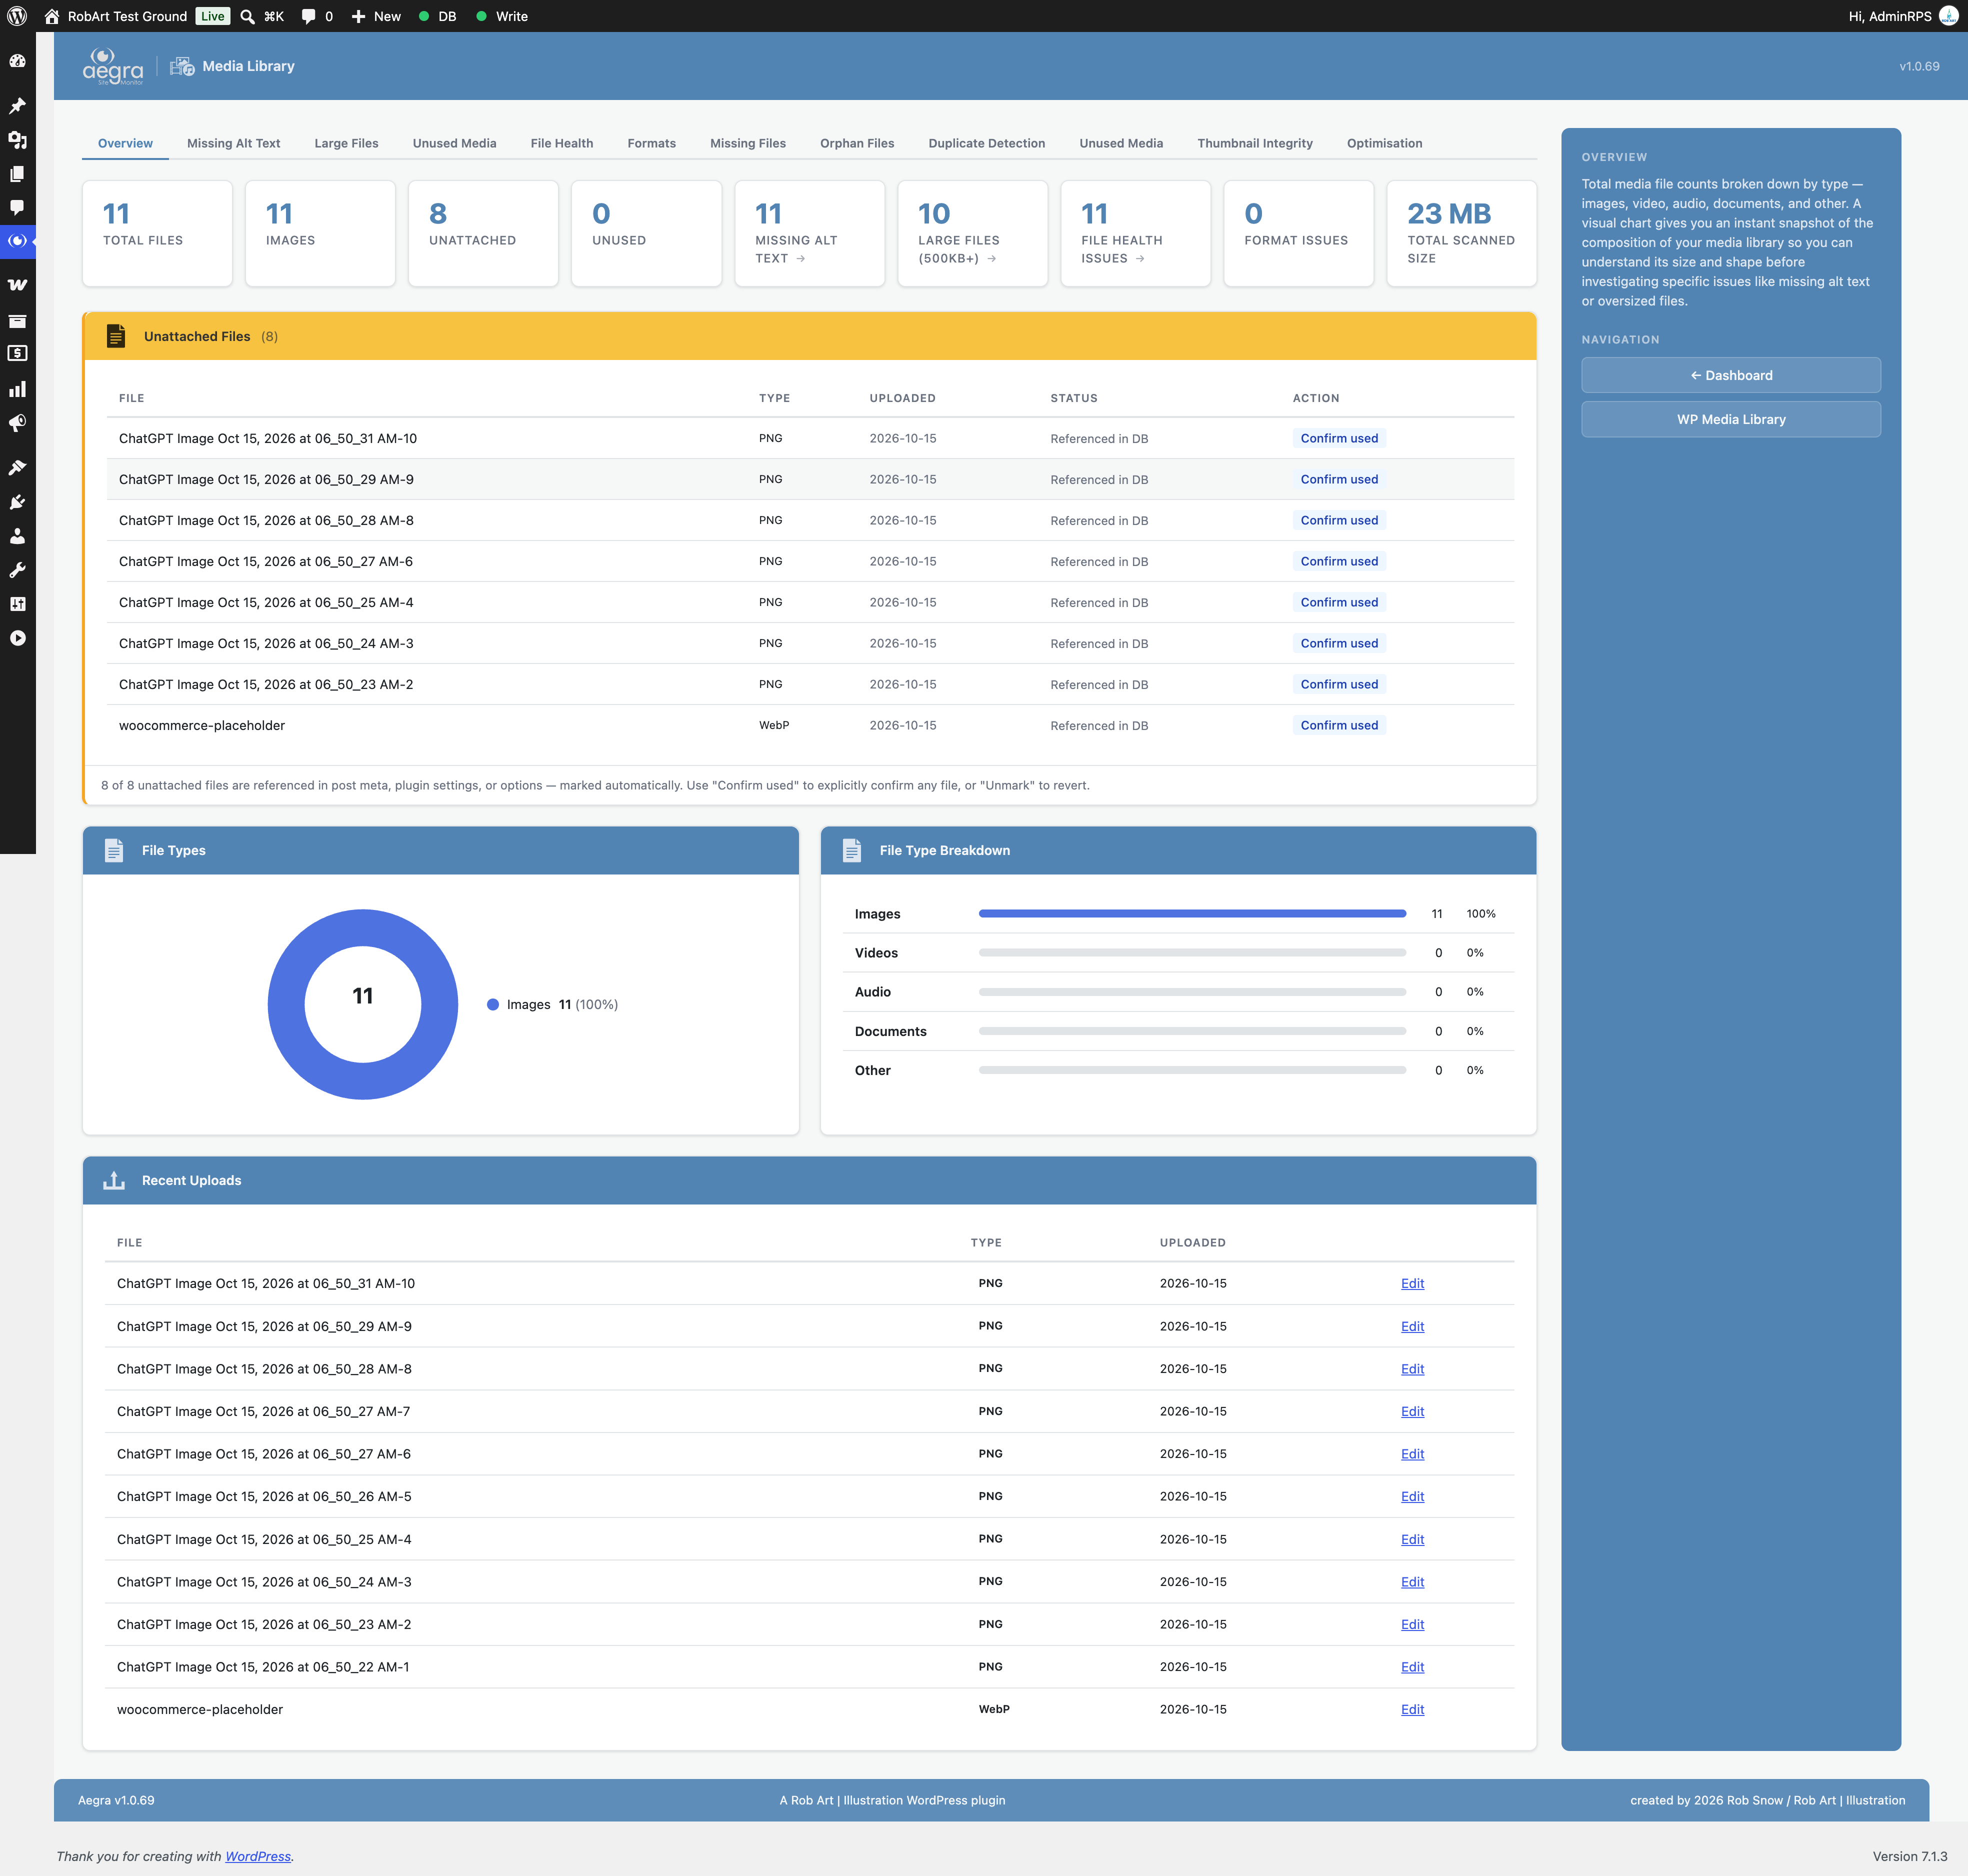
- Media Library: Review file types, media totals and missing alt text.
- Traffic: Explore page views, referrers, devices and visitor countries.
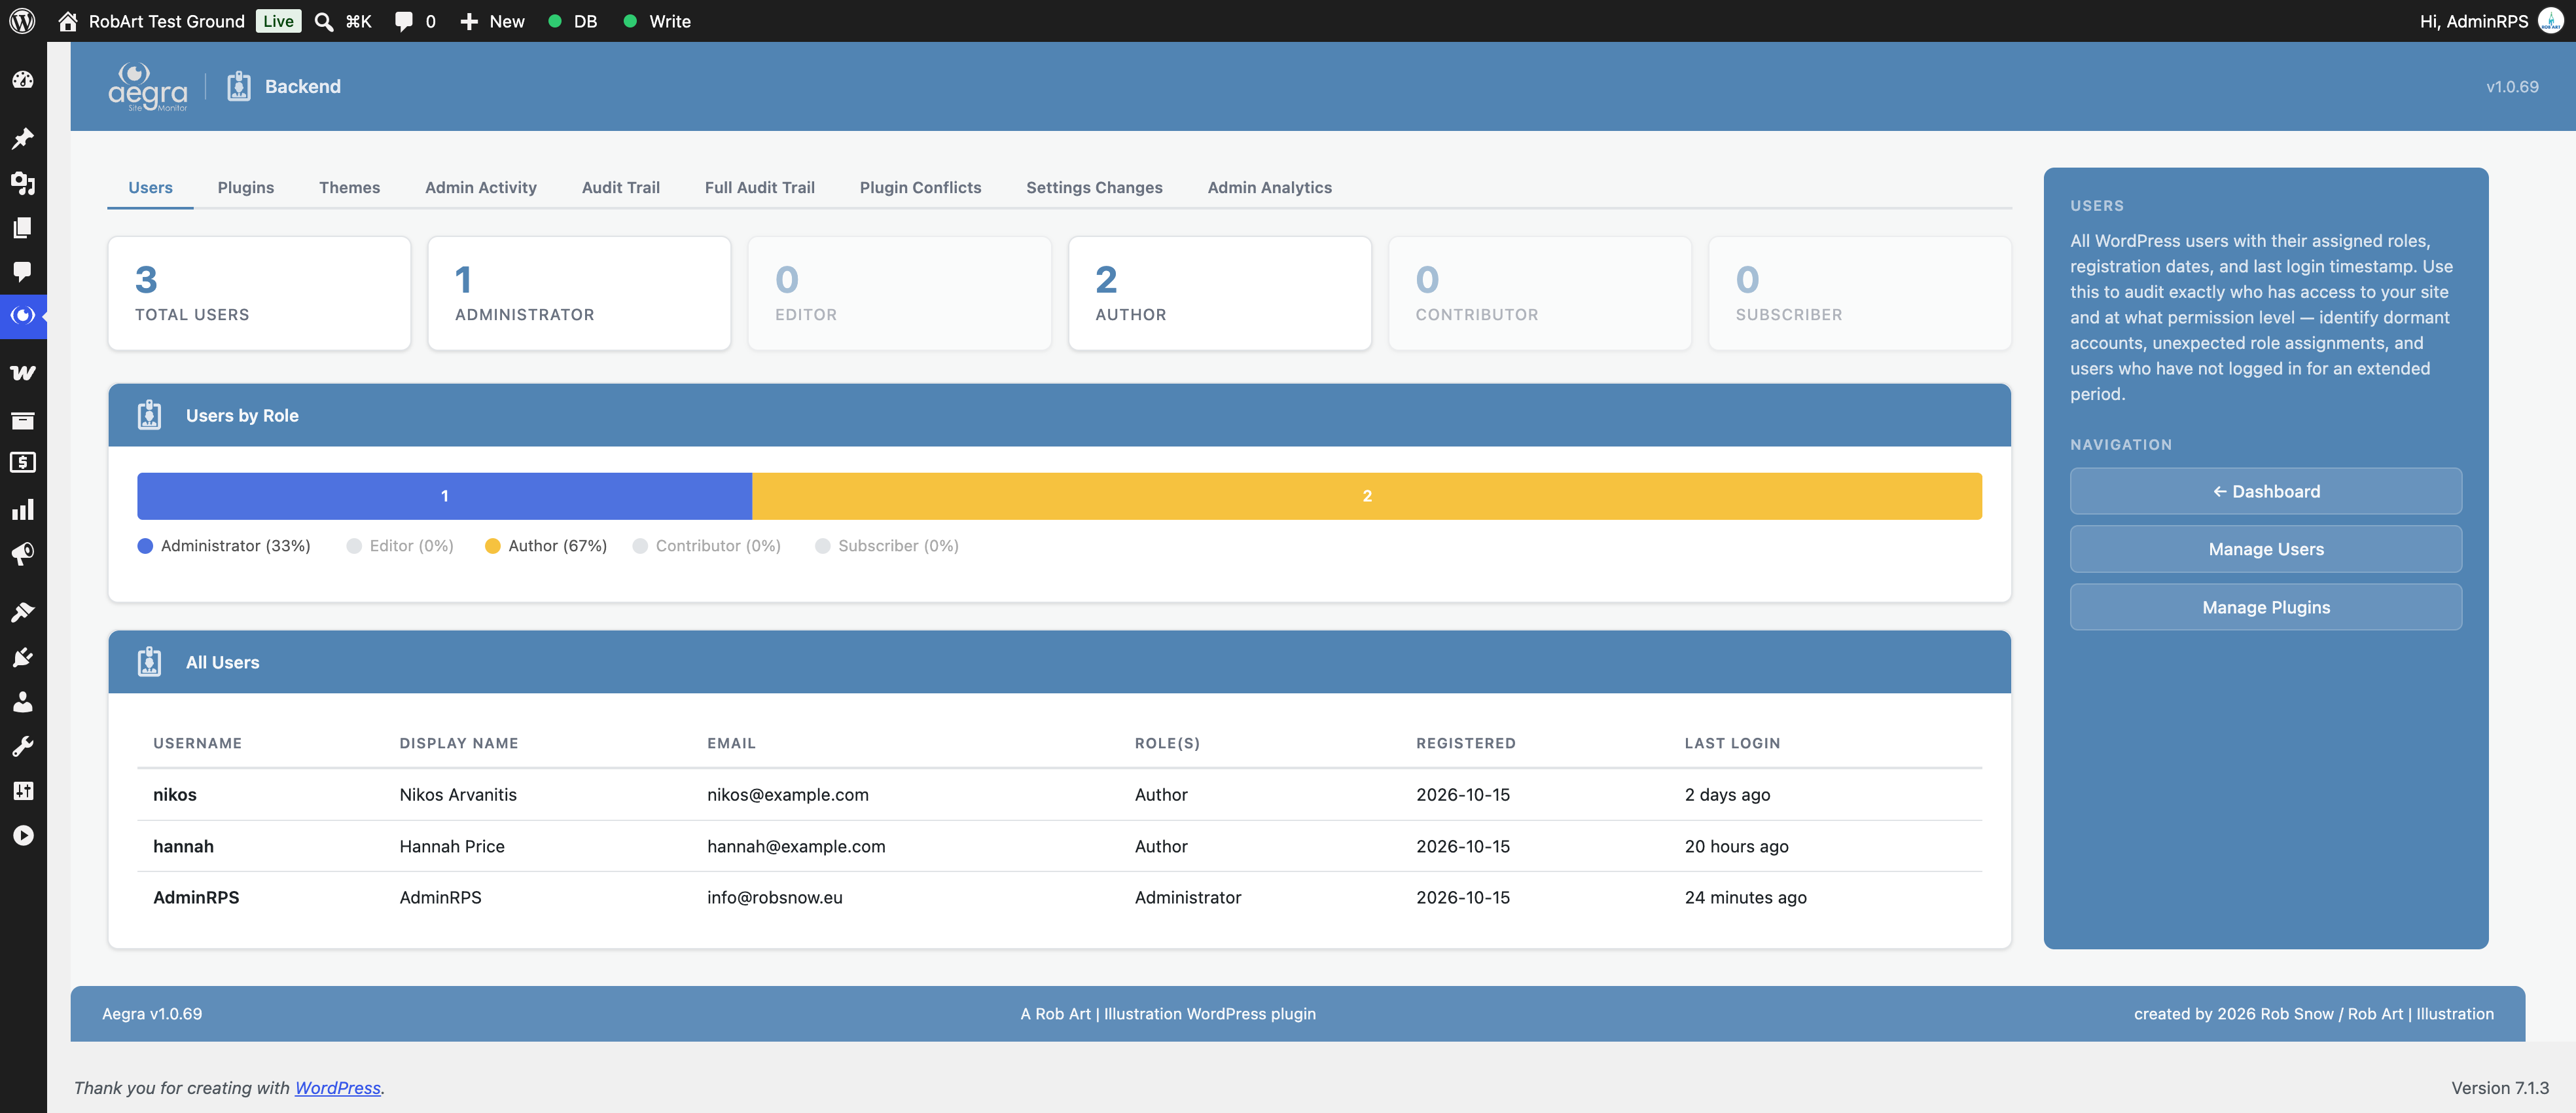
- Users: See user roles and last-login information.
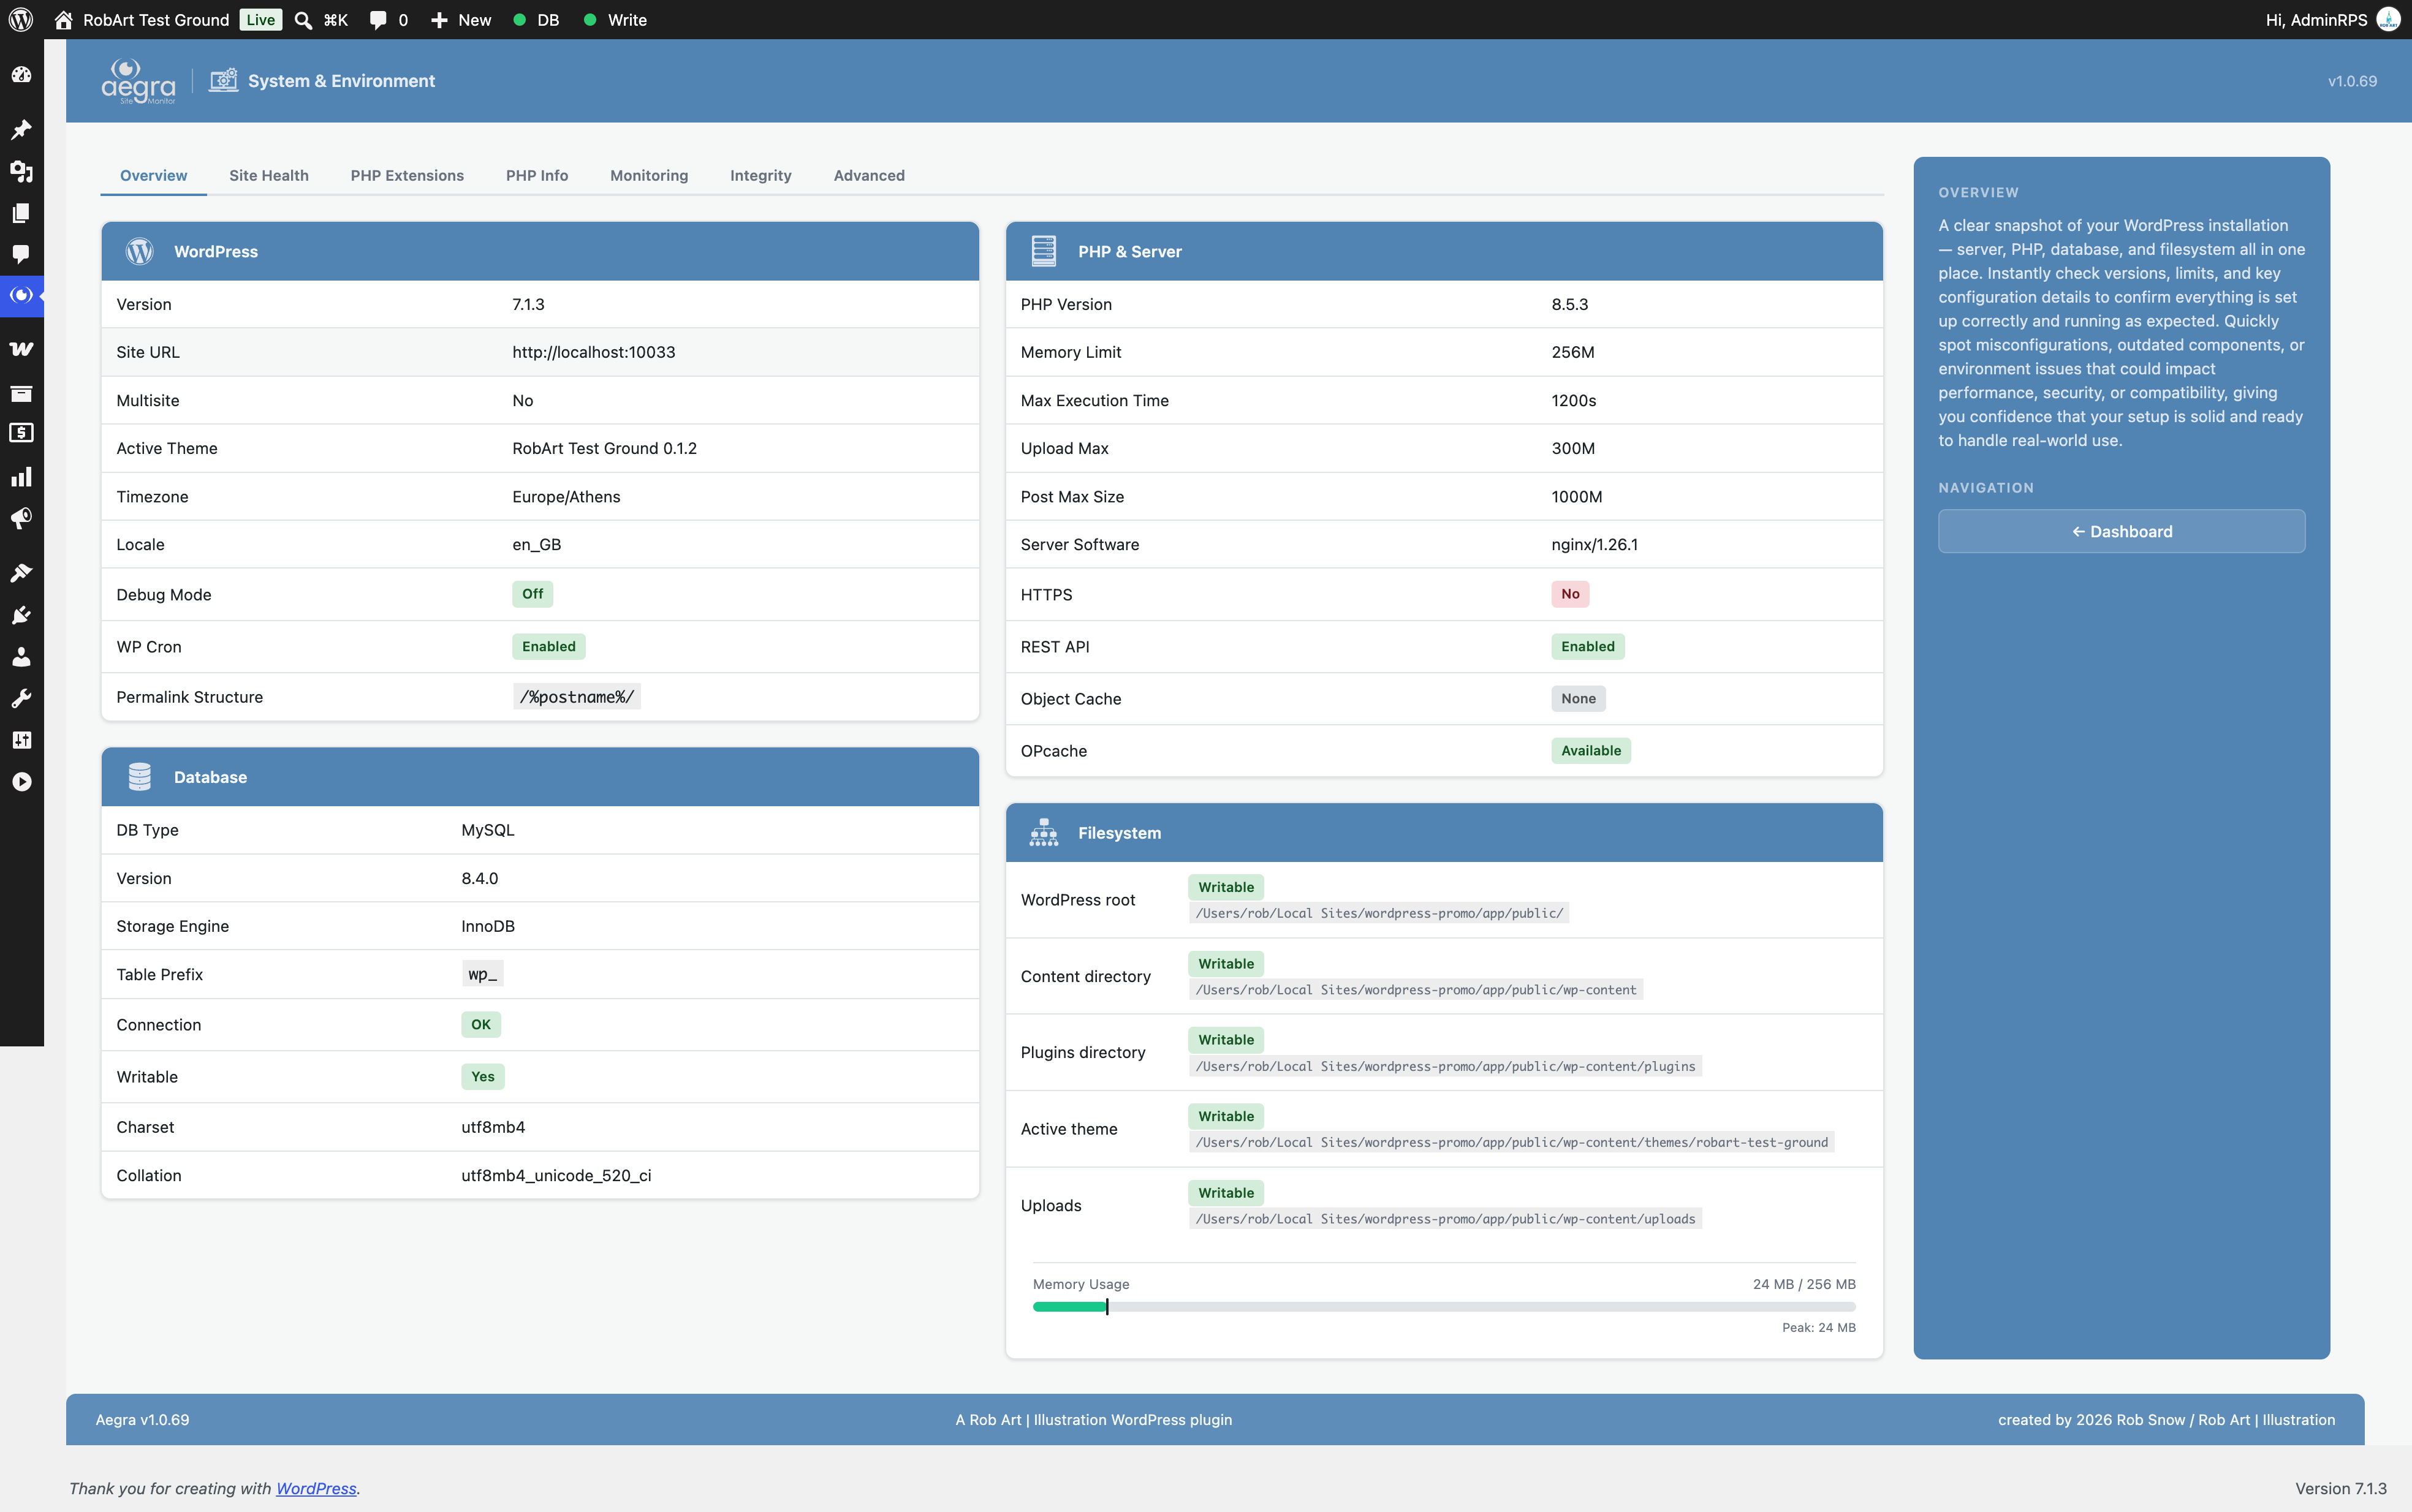
- System: Check WordPress, PHP and server environment details.
- Plugins & Themes: See installed extensions and their update status.
Go Further with Aegra Pro
The free version helps you see the state of your site today. Pro helps you investigate changes over time, catch problems sooner and reduce repetitive checks.
- Full audit trail: Find out who changed what and when.
- Database history: Compare snapshots and investigate slow queries.
- Scheduled checks: Automate scans and reports.
- Alerts: Receive email notifications based on events and thresholds.
- File integrity: Watch for unexpected file changes.
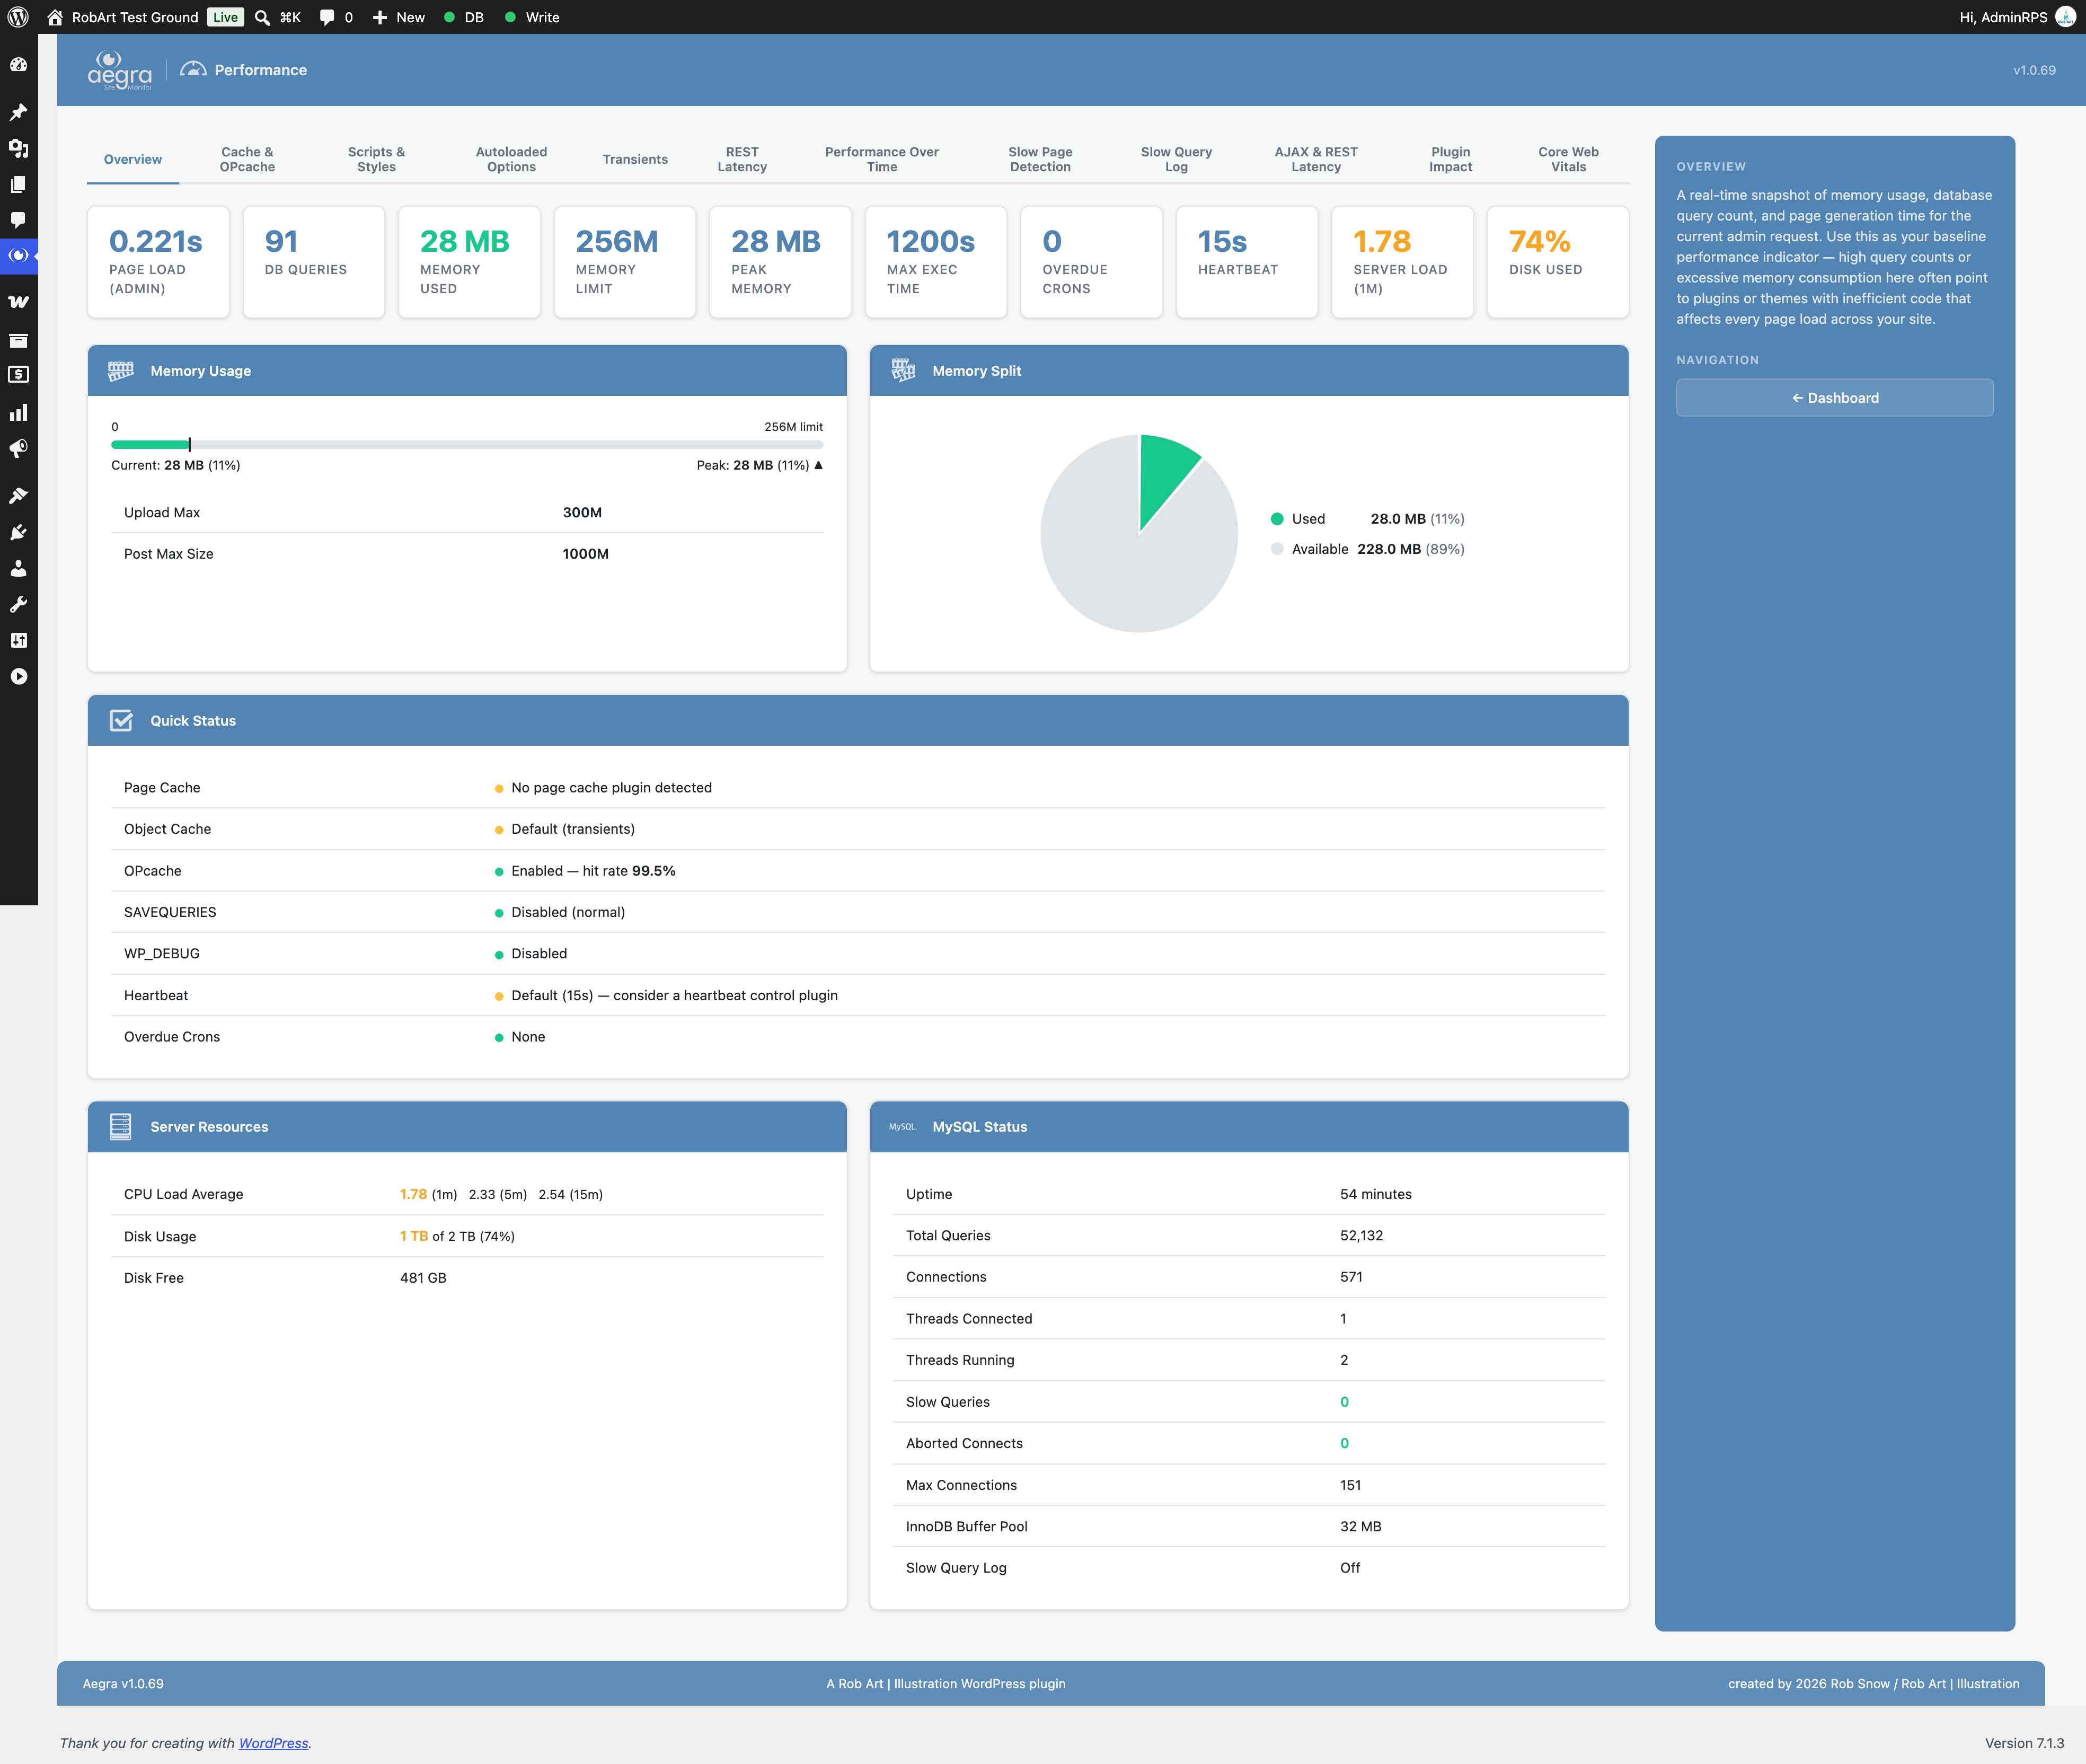
- Performance trends: Follow memory use, AJAX activity and slow pages over time.
- Core Web Vitals: Collect real-world frontend performance metrics.
- Content intelligence: Investigate freshness, orphaned content and SEO structure.
- WooCommerce analytics: Explore deeper store insights.
- Multisite monitoring: Bring network-wide checks into your workflow.
Aegra Site Monitor is built for site owners, freelancers and developers who want a clearer picture of their WordPress installation — whether they manage one site or several.
Uninstall
When you delete Aegra Site Monitor from the Plugins screen, the uninstall script automatically removes all plugin data stored in your WordPress database, including:
- All plugin settings and configuration options
- Licence key and validation data
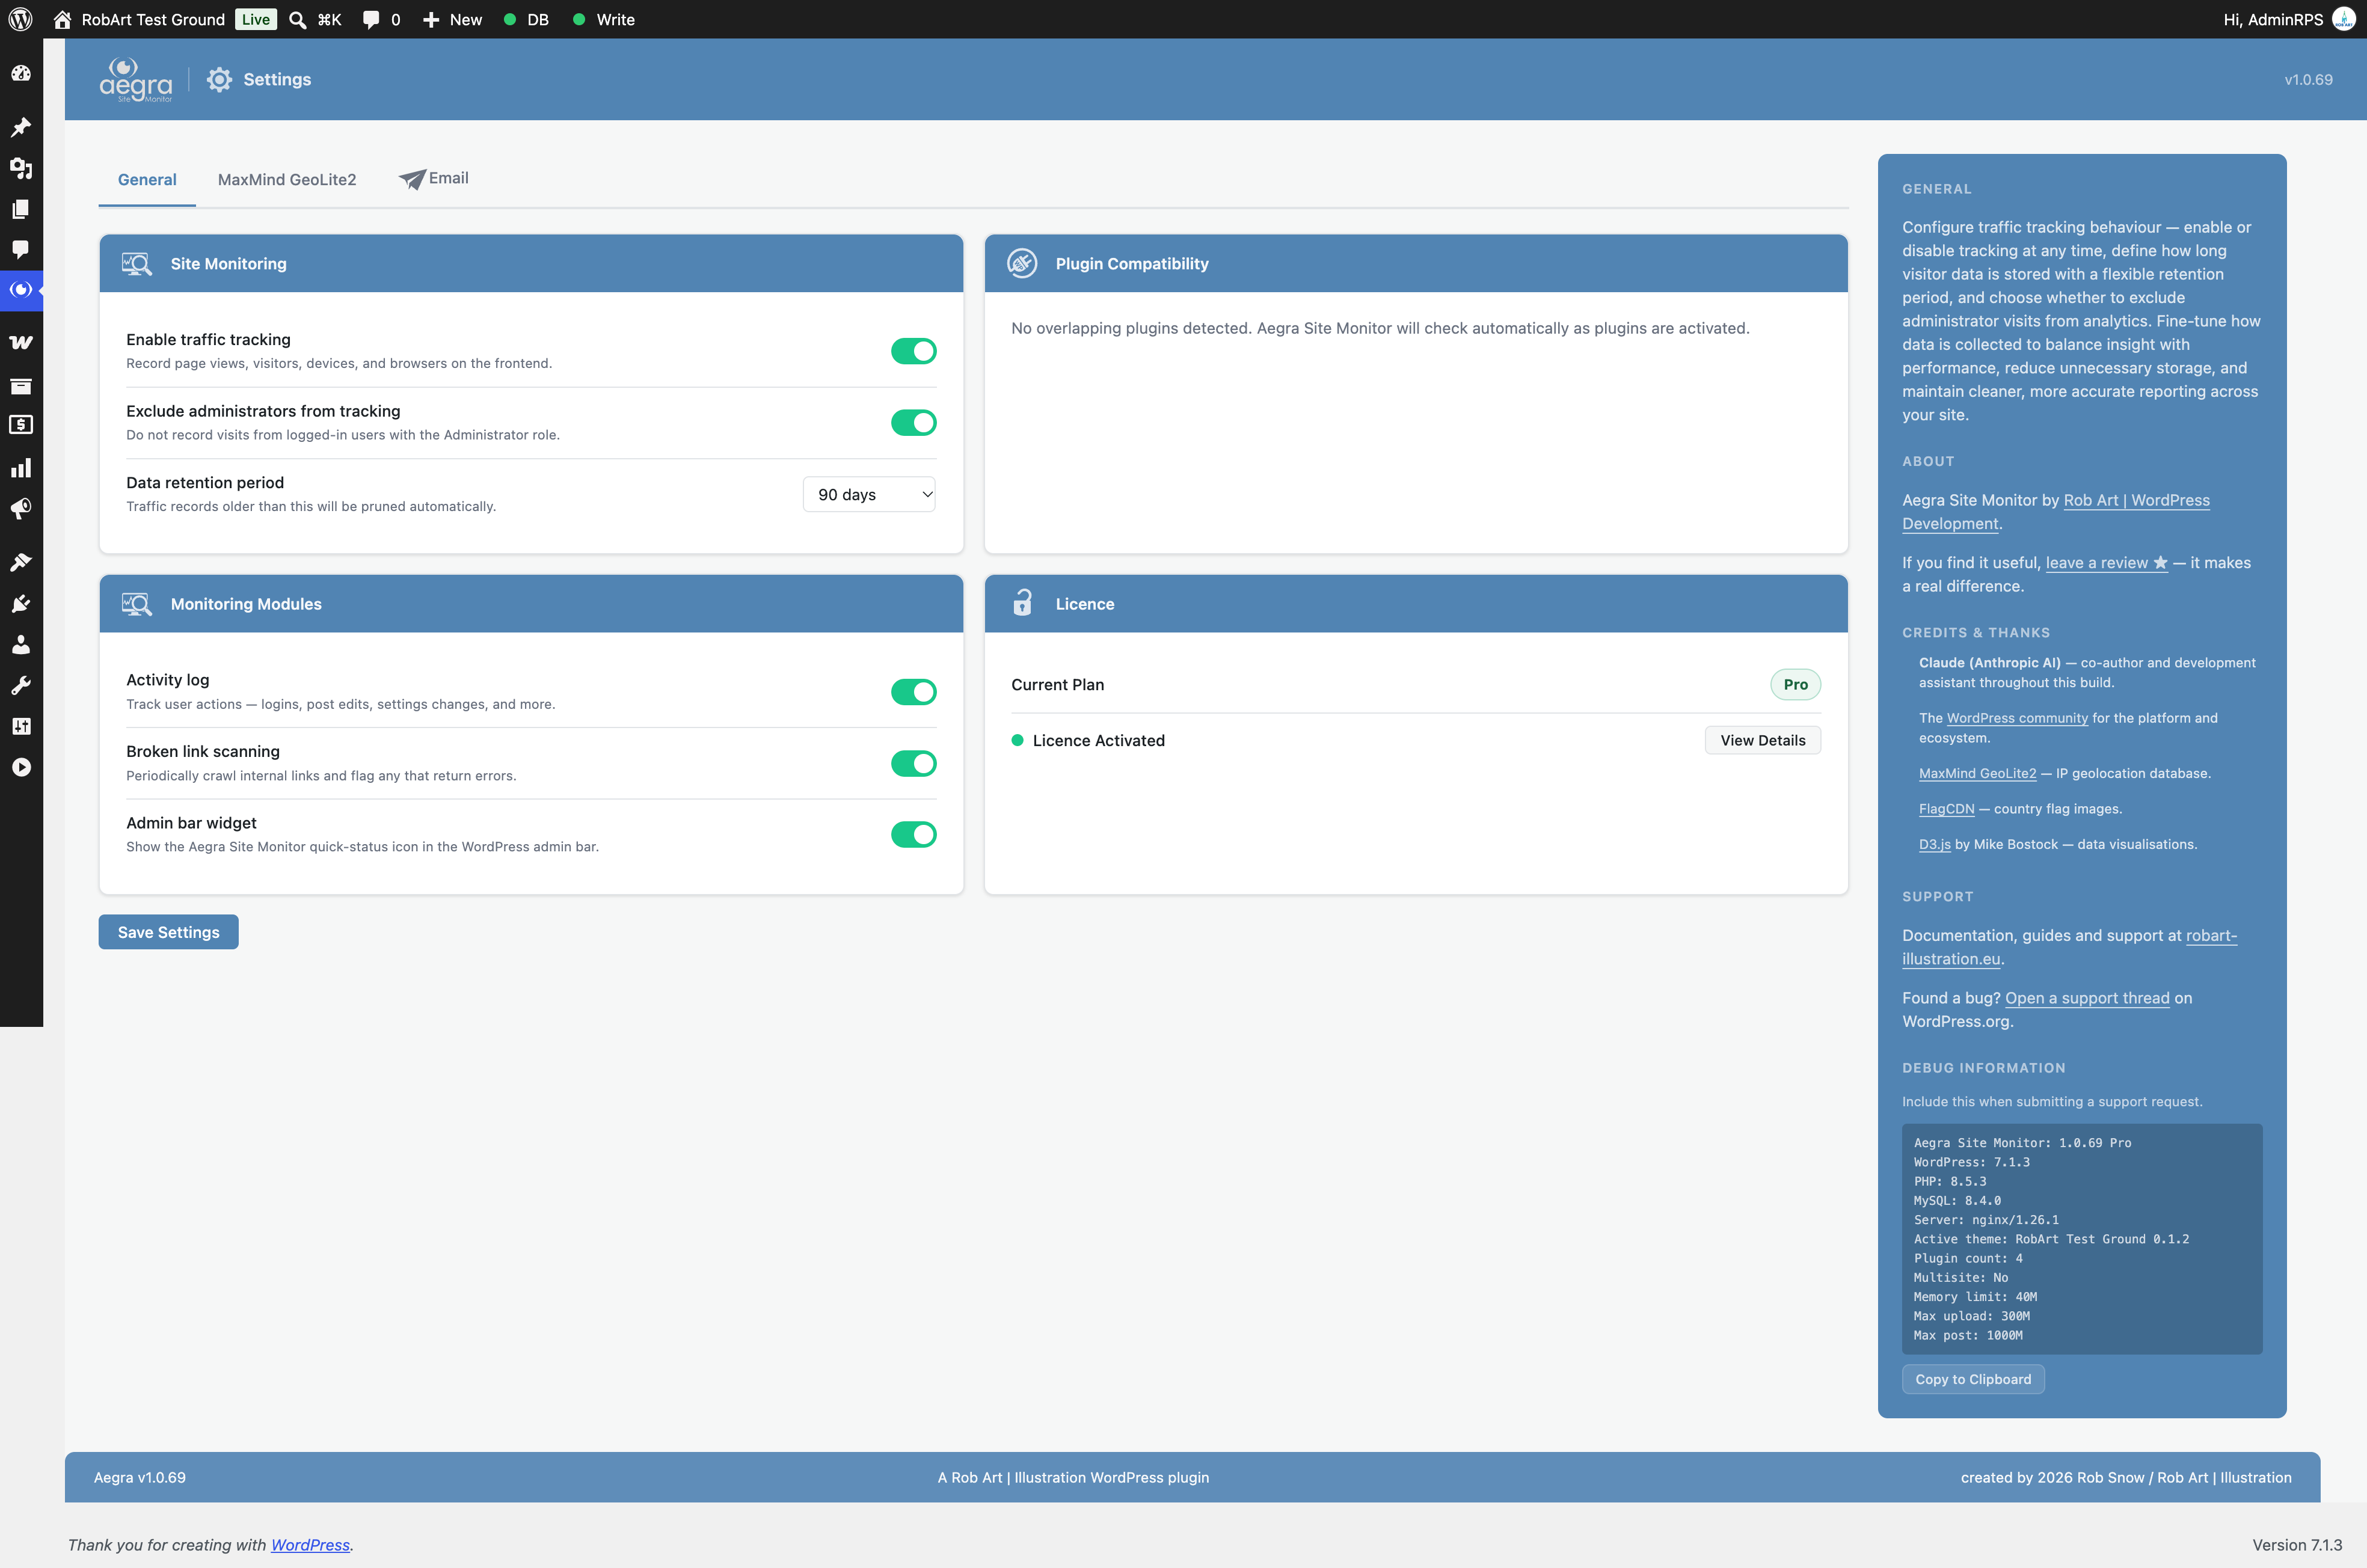
- Traffic tracking settings and recorded visitor data
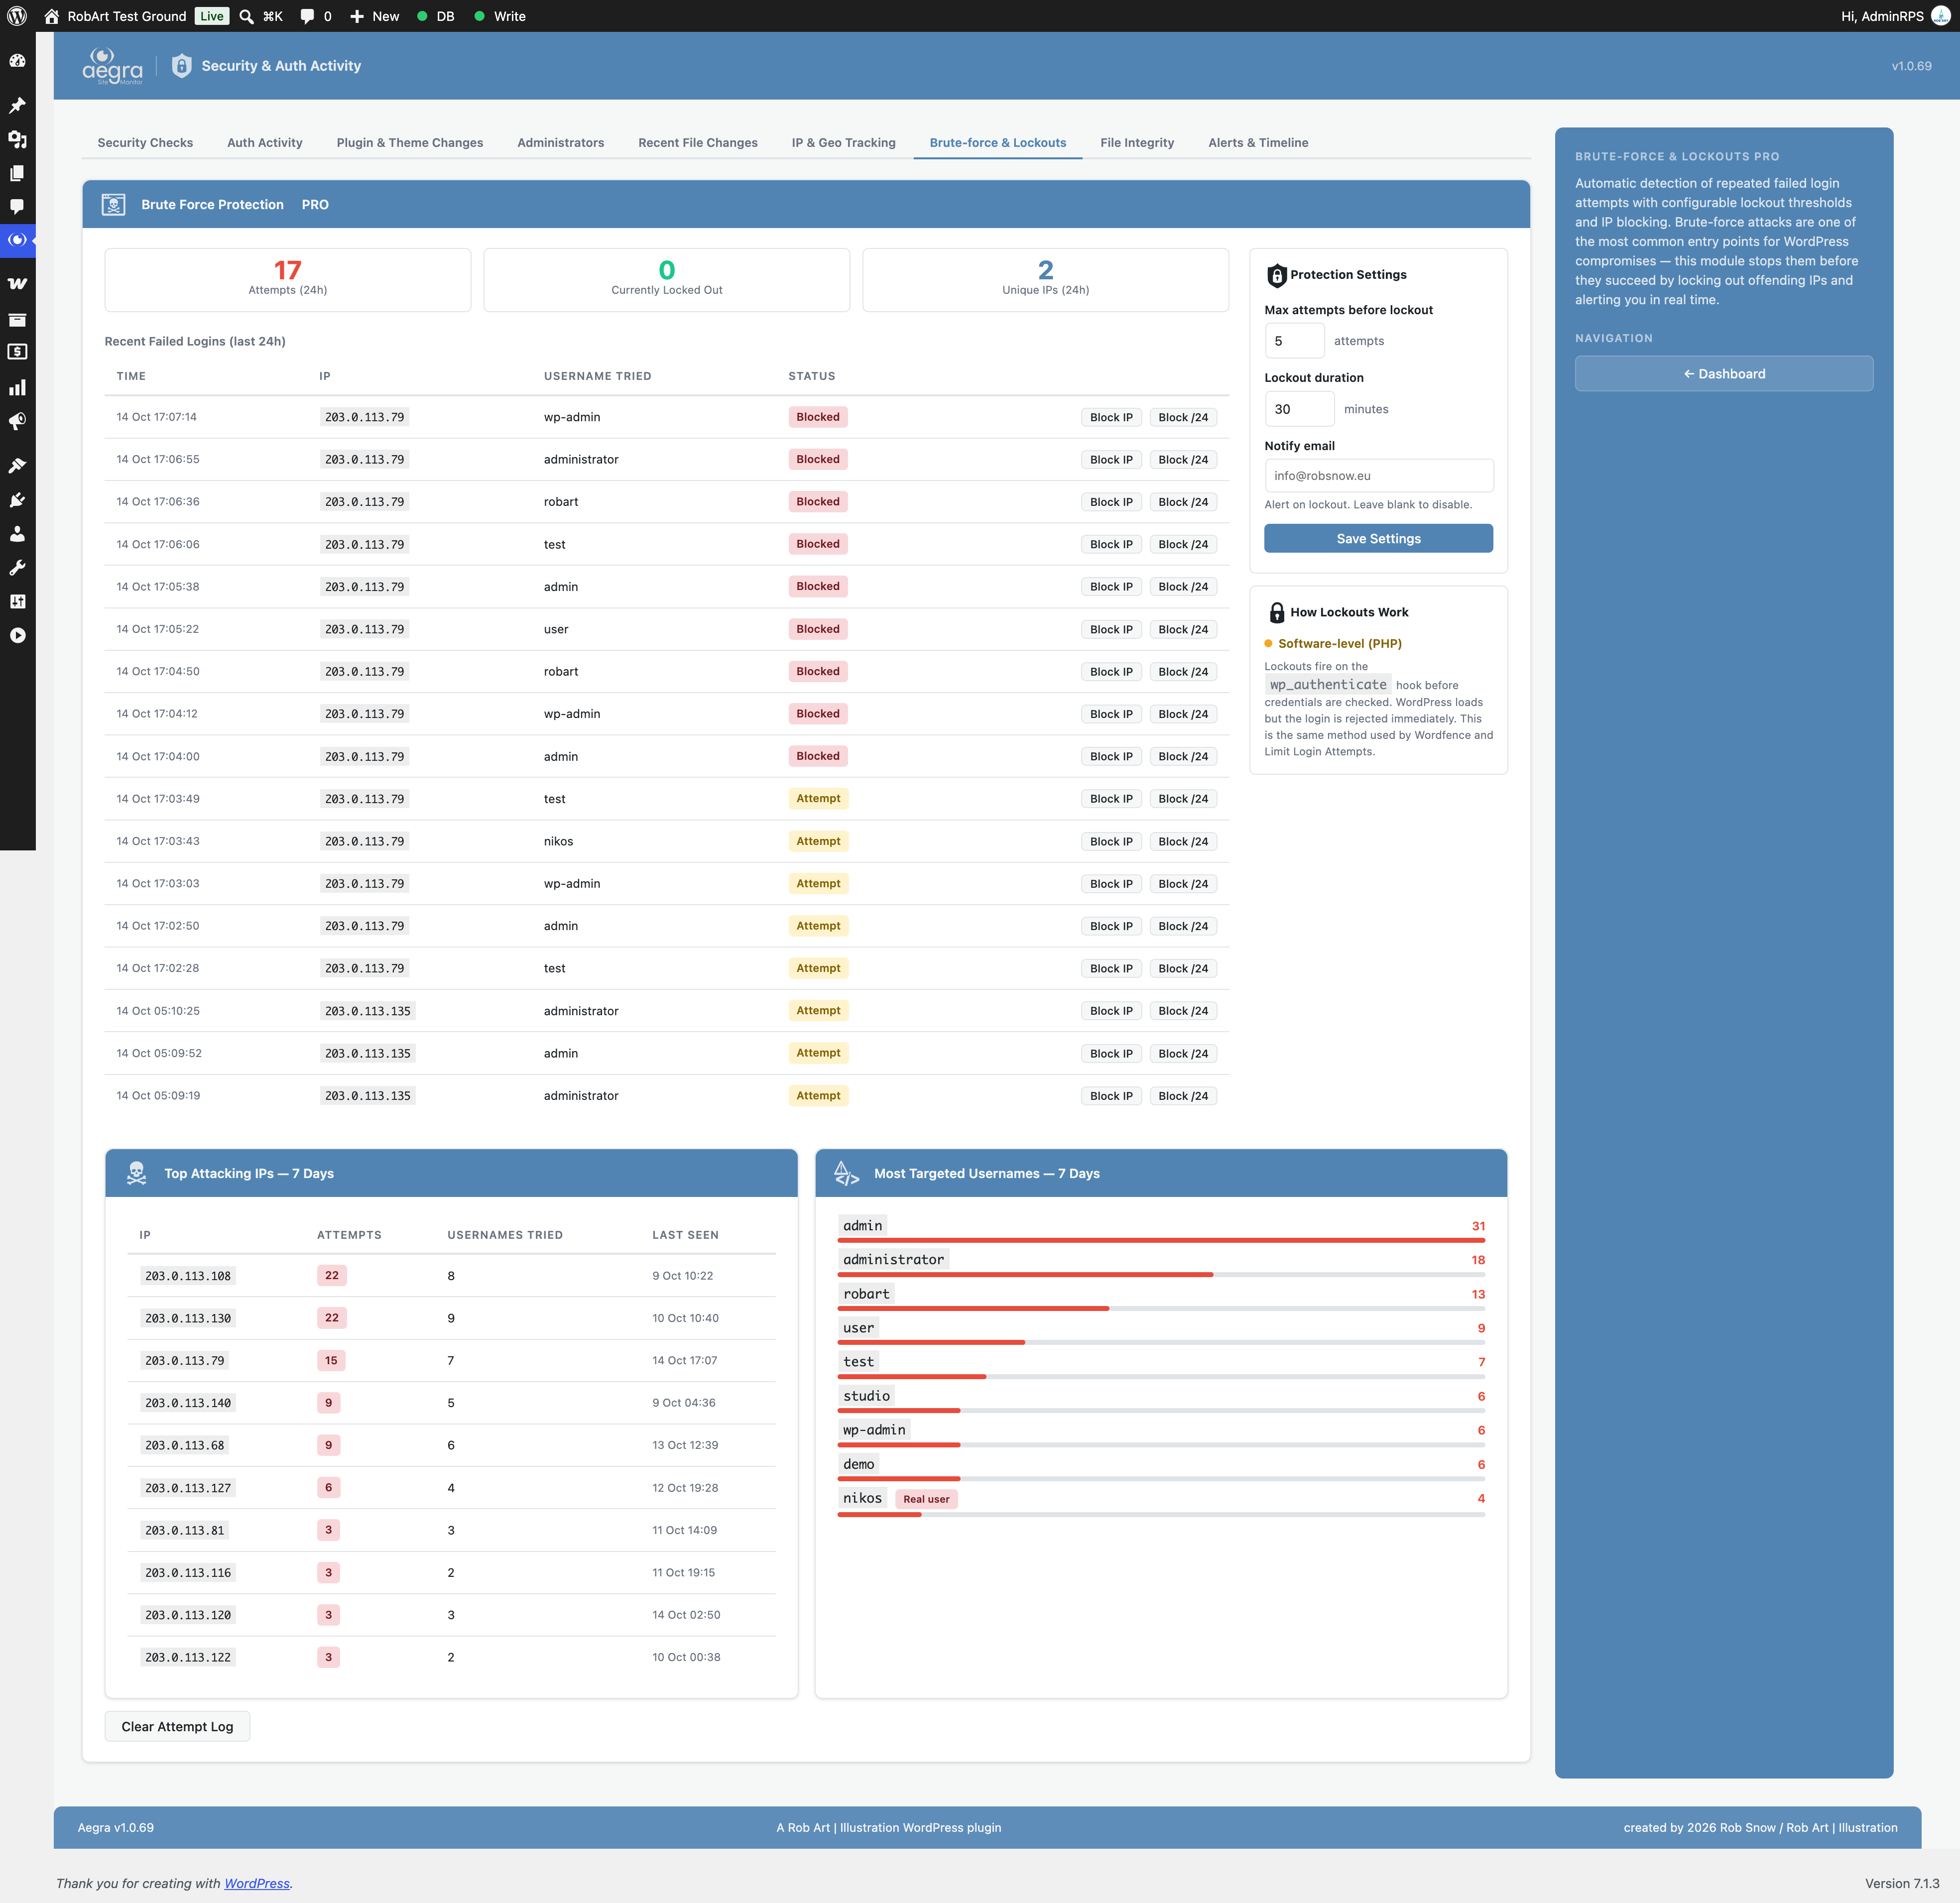
- Security settings, IP block rules, and brute-force records
- Login attempt log
- Activity log and session records
- Broken link scan results
- Performance snapshot history
- Scheduled report configuration
- Media confirmation records
- All cached scan results and authentication transients
- All scheduled cron jobs registered by the plugin
The uninstall script does not delete:
- Any site content (posts, pages, media files, users, etc.)
- The optional MaxMind GeoLite2 database file, if you downloaded one (stored under your uploads directory) — remove it manually if you no longer need it
- Any data held by external services — see the External Services section below for the only outbound connection this plugin makes
Aegra Site Monitor creates four custom database tables (wp_aegra_traffic, wp_aegra_login_attempts, wp_aegra_activity_sessions, wp_aegra_broken_links). All four are fully dropped on uninstall.
External Services
Aegra Site Monitor uses the following external service:
MaxMind GeoLite2 (optional)
The Traffic feature can use the MaxMind GeoLite2 database to show the country of visitor IP addresses. The database is downloaded to your own server only when you choose to enable this feature and provide your own free MaxMind account credentials. When you request the download, the plugin contacts MaxMind to retrieve the database file; your MaxMind account ID and licence key are sent to MaxMind to authenticate that download. During normal operation no visitor data is sent to MaxMind — IP lookups happen locally against the downloaded database. If you never enable this feature, the plugin makes no external requests.
Provided by MaxMind, Inc.:
- GeoLite2 End User License Agreement: https://www.maxmind.com/en/geolite/eula
- Privacy Policy: https://www.maxmind.com/en/privacy-policy
- Website Terms of Use: https://www.maxmind.com/en/terms-of-use
No other data is sent to any external service without your action.
Support
For documentation, guides, and FAQs visit the Help & Documentation page.
For bug reports or feature requests, please use the support forum on the plugin page or contact us via the Aegra Site Monitor plugin page.
Screenshots
Installation
- Upload the
aegra-site-monitorfolder to/wp-content/plugins/ - Activate via Plugins Installed Plugins
- Navigate to Aegra Site Monitor in the admin menu
- Complete the setup wizard to enable monitoring modules
FAQ
-
Does Aegra Site Monitor slow down my site?
-
Aegra is designed to keep overhead low. Traffic is recorded through a lightweight asynchronous request, while most diagnostics run on demand when you open the relevant admin page. As with any monitoring plugin, actual resource use depends on your hosting and site traffic.
-
What is the MaxMind GeoLite2 database?
-
It is a free IP geolocation database used to show visitor countries on the Traffic page. You need a free MaxMind account to download it. The database is stored on your server — no visitor data is sent to MaxMind during normal operation.
-
Where is data stored?
-
All data is stored in your WordPress database in dedicated Aegra Site Monitor tables. Nothing is sent to external servers.
-
How do I remove Aegra Site Monitor completely?
-
Deactivate and delete the plugin via Plugins Installed Plugins. Aegra Site Monitor will automatically remove all database tables and options it created.
Reviews
There are no reviews for this plugin.
Contributors & Developers
“Aegra Site Monitor” is open source software. The following people have contributed to this plugin.
Contributors
Translate “Aegra Site Monitor” into your language.
Interested in development?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Changelog
1.0.70
- Fixed (Pro): brute-force lockouts now actually stop logins. The lockout was checked before WordPress’s own password check, which discarded it, so a locked-out IP could keep trying. Lockouts now also last the set number of minutes on sites not using UTC.
- New (Pro): blocked usernames. Block names used by credential-stuffing bots (wildcards allowed); any IP that tries one is locked out on its first attempt. Real accounts can never be blocked.
- Improved (Pro): alert, lockout and database-scan emails are now styled HTML with a summary table and a link back to Aegra.
- Fixed: the Activity Log could show “No sessions found” on hosts whose MySQL runs in strict mode, even though sessions had been recorded.
- Fixed: Front-end Overview counted Media as 0. Media files are now counted, and kept out of the published totals and coverage bars so they don’t dwarf posts and pages.
- Changed: rewritten plugin description.
1.0.69
- Security: internal hardening.
1.0.68
- Fixed: security alert emails were never sent. A real attack (brute-force lockout, a blocked IP or country, a file-integrity change, a new or promoted administrator) now emails you, even though the test email had always worked.
- Fixed: the brute-force lockout notice now defaults to your site admin email instead of staying silent until a notification address was entered by hand.
- New: file-integrity scans and new-administrator events now raise alerts; critical security alerts are on by default so a fresh install is protected without extra setup.
1.0.67
- Fixed: the Reports screen showed XML-RPC as Enabled on sites that block xmlrpc.php at the server, for example in .htaccess. Aegra now tests whether xmlrpc.php really answers (once an hour) and shows “Disabled or blocked”.
- New (Pro): Media > Orphan Files lists files in the uploads year/month folders that no media item owns, often left behind by image converters and optimisers. Files still mentioned in a post, custom field or setting are kept. Chosen files move to a holding folder closed to the web, where they can be put back or deleted for good.
1.0.66
- Fixed: Recheck on the Broken Links screen only asked for the same address again, so a link you had already replaced or removed stayed on the list. It now checks the post as it is today, and a link that is no longer there drops off the list.
- New: images protected by Robart Image Guard no longer show as broken links. Links to the original file, or any of its sizes, are marked “Protected” and left out of the broken count. Recheck or rescan to update links already on the list.
- Fixed: the Transients count included each transient’s expiry record, roughly doubling it, and warned “High” above 200 even when none had expired. Live transients are working caches, so only expired ones are now flagged.
- Fixed: “Collation Mismatches” flagged tables that only sort a few accented letters differently, which is harmless. It is now “Character Set Mismatches”, flags only tables that store text in a different character set, and names them.
- Changed: “Trashed Posts” is now “Binned Items (all types)”, as it counts the bin of every content type, not only posts.
- Improved: MaxMind setup. Spaces and invisible characters pasted with a licence key are removed, and when MaxMind refuses the details Aegra shows MaxMind’s own reason and what it sent (account ID, and the key’s length and last four characters), so the problem can be found.
- Improved: installing the MaxMind database by hand. Settings now shows the exact folder to upload GeoLite2-City.mmdb to, prepares and protects that folder, and confirms when the file is found, with its size and age.
- Fixed (Pro): Live Traffic showed the theme’s “Page not found” title for 404 visits. It now shows the address that was requested.
- Fixed (Pro): Thumbnail Integrity reported image sizes as missing that WordPress would never create for that image (for example the large sizes of a small image), and counted SVG files. Each image is now judged against the sizes WordPress actually makes for it.
- Fixed (Pro): Database Optimisation. Binned items are broken down by content type with a link to each bin; Duplicate Postmeta only lists true duplicates, not the earlier slugs and dates WordPress keeps on purpose for redirects; Table Overhead ignores the space every table normally keeps in reserve, and Optimize Tables only rebuilds the tables it lists.
- Fixed (Pro): Plugin Impact always showed 0.0 queries. Queries are now measured on 1 in 20 front-end page views and credited to the plugin that made them, which also means Aegra records far less on ordinary page views.
- Fixed (Pro): the File Integrity screen could run out of memory, because every changed file from the last 20 scans was kept. The newest scan keeps 1,000 files and older scans 100, suspicious and modified files first, with the full counts. A history already too large to load is cleared once, keeping your baseline.
- Fixed (Pro): the Unused Media screen ran a malformed database query every time it opened.
1.0.65
- Security: Aegra trusted “forwarded” address headers sent by any visitor, so a visitor could claim to be any address they liked — slipping past IP blocks, appearing as an allowlisted address, or putting an address of their choosing into the login log. These headers are now believed only when the request genuinely comes through Cloudflare, your host’s own proxy, or a proxy you list in wp-config.php (AEGRA_TRUSTED_PROXIES).
- Security: country blocking could be avoided by sending a false country header. The country is now only taken from that header when the request really comes through Cloudflare.
- Safety: Aegra never blocks, counts or locks out your own server’s address or a proxy’s, so a block can no longer shut out every visitor (including you) at once.
- Fixed: blocking an IPv6 address range had no effect — range matching only understood IPv4. Both now work.
- Improved: the country blocker listed only 59 countries. All 250 are now available, and the same complete list is used throughout Aegra.
- New: the IP & Geo Blocking screen shows the address Aegra sees for you, and how it worked it out, so you can confirm it matches your real address.
1.0.64
- Fixed: Traffic statistics counted search-engine and crawler visits as real visitors, so the Overview tab reported far more views and unique visitors than the Sessions tab did for exactly the same period. Bot traffic is now excluded from every traffic figure and chart, and the two tabs agree.
- Fixed: the same problem affected the daily views chart, referrers, devices, browsers and the country breakdown — crawlers were counted alongside real people, which is why a data-centre visitor could appear as a phone. All of these now show human visitors only.
- Fixed: the “Bots Blocked” figure counted every blocked request rather than the number of bots, so a single crawler visiting many pages could read as hundreds. It is now labelled “Bot Requests Blocked” and shows how many separate crawlers those requests came from.
- Fixed: crawler visits were recorded under a web-browser name — Googlebot was stored as Chrome, and most others simply as “Other”. Crawlers are now recorded by name, so the bot breakdown is accurate. Visits recorded before this update keep their old labels, so the crawler count builds up as new traffic arrives.
1.0.63
- New: the Brute-force log now has “Block IP” and “Block /24” buttons on every failed-login row, so an attacking address — or the whole range it sits in — can be added to the IP & Geo blocklist in one click. Rows already blocked say so instead of offering a duplicate.
- Fixed: adding an IP to the blocklist did not check that it was a valid address. A malformed entry was written straight into the server access rule, which could take the whole site down. Addresses and ranges are now validated before anything is written.
- Fixed: it was possible to block your own address, or a range containing it, and lock yourself out of your own site. This is now refused with an explanation.
- Fixed: blocking a range wrote a directive older servers could not read, so the block silently did nothing on those hosts. Ranges are now written in a form both modern and older servers understand.
- Fixed: notes saved against a blocked address could display with stray backslashes. New notes are stored correctly and existing ones are tidied automatically.
- Fixed: on the File Integrity screen the side panels were clipped by the information panel, and long file paths pushed the results table out of shape. The layout now holds at any width and paths wrap instead of overflowing. The same layout fix was applied to the other security screens that share the pattern.
- Fixed: the Sessions traffic chart only drew bars for days that had visitors, so a quiet month appeared as a handful of enormous blocks and the spacing between them was meaningless. Every day in the period is now shown, quiet days included, with dates along the bottom and the busiest day’s total beside the title.
1.0.62
- Fixed: a critical issue in the Pro IP-blocking feature where blocking any IP address could make the whole site return “403 Forbidden” to every visitor. The server access rule is now written correctly so it denies only the blocked addresses while allowing everyone else.
- Fixed: the site’s own internal requests (scheduled tasks, loopback and server-side calls) are no longer counted as visitor traffic or as failed login/brute-force attempts, so your statistics and security logs reflect real visitors only. The server’s own IP can be recorded in settings to reinforce this on hosts that don’t expose it automatically.
- Fixed: hardened output escaping and input sanitising across the admin dashboards and Pro modules for stricter WordPress.org compliance.
1.0.61
- Fixed: visitor country detection, country geo-blocking and login brute-force protection now use the real visitor IP address behind a reverse proxy or managed host. Previously they could read the hosting proxy’s address instead, which mislabelled visitor countries (e.g. showing the datacentre’s country), applied country blocks to the wrong country, and made all proxied visitors share one brute-force lockout. Also added a live self-test to the GeoIP status that verifies country lookups actually resolve, not merely that the database file is present.
1.0.60
- Fixed: on the WordPress Dashboard “Aegra Site Monitor” widget, the section-header links (“View full”, “Manage”, etc.) could appear dark blue on the blue header and be hard to read; they are now clearly legible on every link state. The same header links on Aegra’s own dashboard were hardened against the same issue.
1.0.59
- Fixed: the shared MaxMind (GeoIP) folder used a
.phpfile as its directory guard; it now uses an inertindex.html, so nothing executable is written into the uploads area. No change to how the GeoIP database is stored or used.
1.0.58
- Translation-ready: the entire admin interface — the dashboard, every section page, the setup wizard, notices and menus — is now fully internationalised, so Aegra can be translated into any language. The translation template ships with around 1,000 strings.
- Housekeeping only — no change to how anything works.
1.0.57
- Fixed the admin tabs briefly flashing the first tab (Overview) after running a scan or action — the correct tab now stays selected, on every tabbed page
- Confirmed compatible with the current version of WordPress
1.0.55
- GeoIP: the MaxMind GeoLite2 database now installs to a single shared location under the uploads directory, so it is reused rather than downloaded separately by each plugin that needs it, and it remains available if another plugin is removed
- GeoIP: location detection now correctly falls back to the plugin’s own database when another analytics plugin that previously supplied one has been removed (it no longer reports a database as in use after that plugin is gone)
- Visitor Map (Pro): the live map now runs entirely on Aegra’s own visitor data and GeoIP database, with no dependency on any other analytics plugin
- Fixed a display issue where the lock badge on Pro feature previews could be clipped
- Media: the Duplicate Filenames list now shows the attachment IDs as clickable edit links instead of raw markup
1.0.54
- Fixed the Pro “Verify & Activate” licence button: the licence-key field was being stripped from the settings page, which prevented activation. The licence card now renders its form correctly.
- Broken link scanner — major accuracy and reliability improvements:
- Links that work in a browser are no longer wrongly reported as broken. The scanner now retries with a full GET request when a HEAD request fails, uses a real browser identity, and no longer flags pages that simply block automated requests (such as Facebook or LinkedIn).
- The scan is faster (smaller batches, shorter per-link timeout, partial downloads) and no longer stalls or shows an unstable link count when run repeatedly.
- Added a live progress indicator with a spinner and a running “links checked” count, so it is clear the scan is working on large sites.
- A scan that is interrupted (for example by deactivation) no longer leaves the screen stuck on “Scanning…”.
1.0.53
- Updated the “Get Pro” / upgrade links to the current checkout address
1.0.52
- Composed the WordPress core file-editor AJAX action name from its standard parts when attaching the activity-log listener, to make clear the plugin observes a core action rather than defining its own (no functional change)
1.0.51
- Security/compliance hardening pass to meet WordPress.org review requirements:
- Added explicit nonce verification to the activity logger’s file-edit and attachment-change observers (verifying WordPress core’s own nonces)
- Converted all remaining database queries to fully prepared statements using $wpdb->prepare() with %i identifier and %s/%d value placeholders (no interpolated SQL)
- Renamed internal local variables that collided with WordPress global names (e.g. $role, $path, $action) to plugin-prefixed names
- Wrapped filesystem path references in wp_normalize_path() for cross-platform correctness
- Escaped a previously unescaped diagnostic output string
1.0.50
- Renamed the internal code prefix to “aegra” throughout (functions, classes, constants, options, hooks, CSS, and database table names) for full naming consistency
- Database queries now use the %i identifier placeholder via $wpdb->prepare() for all table names (requires WordPress 6.2+)
- Broken-link scanner: internal vs external links are now classified by host (ignoring http/https and www), fixing same-site links being flagged external
- UI: the toggle switch “on” state is now green for clearer visibility
- Raised “Requires at least” to WordPress 6.2
1.0.49
- Output escaping: removed every phpcs:ignore suppression of output-escaping; all icon and HTML output now uses real escaping functions (wp_kses / wp_kses_post)
- Fixed SVG icons rendering at the wrong size — restored the viewBox attribute that the kses pass had lowercased
- Fixed status-card and PHP Info output that displayed as raw markup instead of rendering
- Removed a leftover internal constant and other traces of the project’s former name from the codebase
1.0.48
- WordPress.org compliance and security hardening pass:
- Escaped all output late with the context-appropriate functions (esc_html / esc_attr / esc_url / wp_kses_post)
- Database queries now use $wpdb->prepare() for all values; table-name interpolation justified inline
- Sanitised and unslashed all admin request input; nonce values are sanitised before verification
- Scoped the GeoLite extraction’s ini_set to that routine and restore the original value afterwards
- Renamed leftover internal identifiers to the plugin’s own prefix
- Corrected the plugin header URL
1.0.47
- Renamed the plugin to Aegra Site Monitor, with a descriptor that states its purpose
- Separated all Pro features into a dedicated package — the free version now ships no premium feature code and no licence machinery
- Removed locked Pro controls from the free build; upgrade prompts are now plain adverts that link out to the product page
- Added a dedicated “Get Pro” link on the Plugins screen and a clearer upgrade experience
- Hardened input sanitisation and output escaping throughout
- Moved all generated files into the WordPress uploads directory (nothing is written outside it)
- Aligned the text domain with the plugin slug and regenerated the translation template
- Documented the optional MaxMind GeoLite2 service used by the Traffic feature
- Numerous admin UI fixes, chart and layout polish, and accessibility improvements
- Passes Plugin Check with no errors or warnings
1.0.12
- WordPress 7.0 compatibility — restored familiar form, button, checkbox and radio styling that WP 7.0 changed
- Replaced hardcoded Tailwind blue (#3b82f6) with Aegra Site Monitor brand blue across all pagination, filter pills, charts, and progress bars
1.0.11
- Fixed filter navigation on Campaigns, Advanced, Audit Trail, Admin Analytics, Orphaned Content, and Content Freshness — now preserves correct page and tab
- Fixed Backend > Full Audit Trail select dropdown arrow overlapping text
- Fixed Traffic > Daily Views card not rendering on page load
- Fixed tab switcher always activating first tab to prevent D3 chart zero-width issue
- Changed Dashboard > Activity Log capped at 8 entries
- Changed Traffic > Audience countries now show full name with code beneath
- Changed Live Visitor Map dots now reduce in size as they age
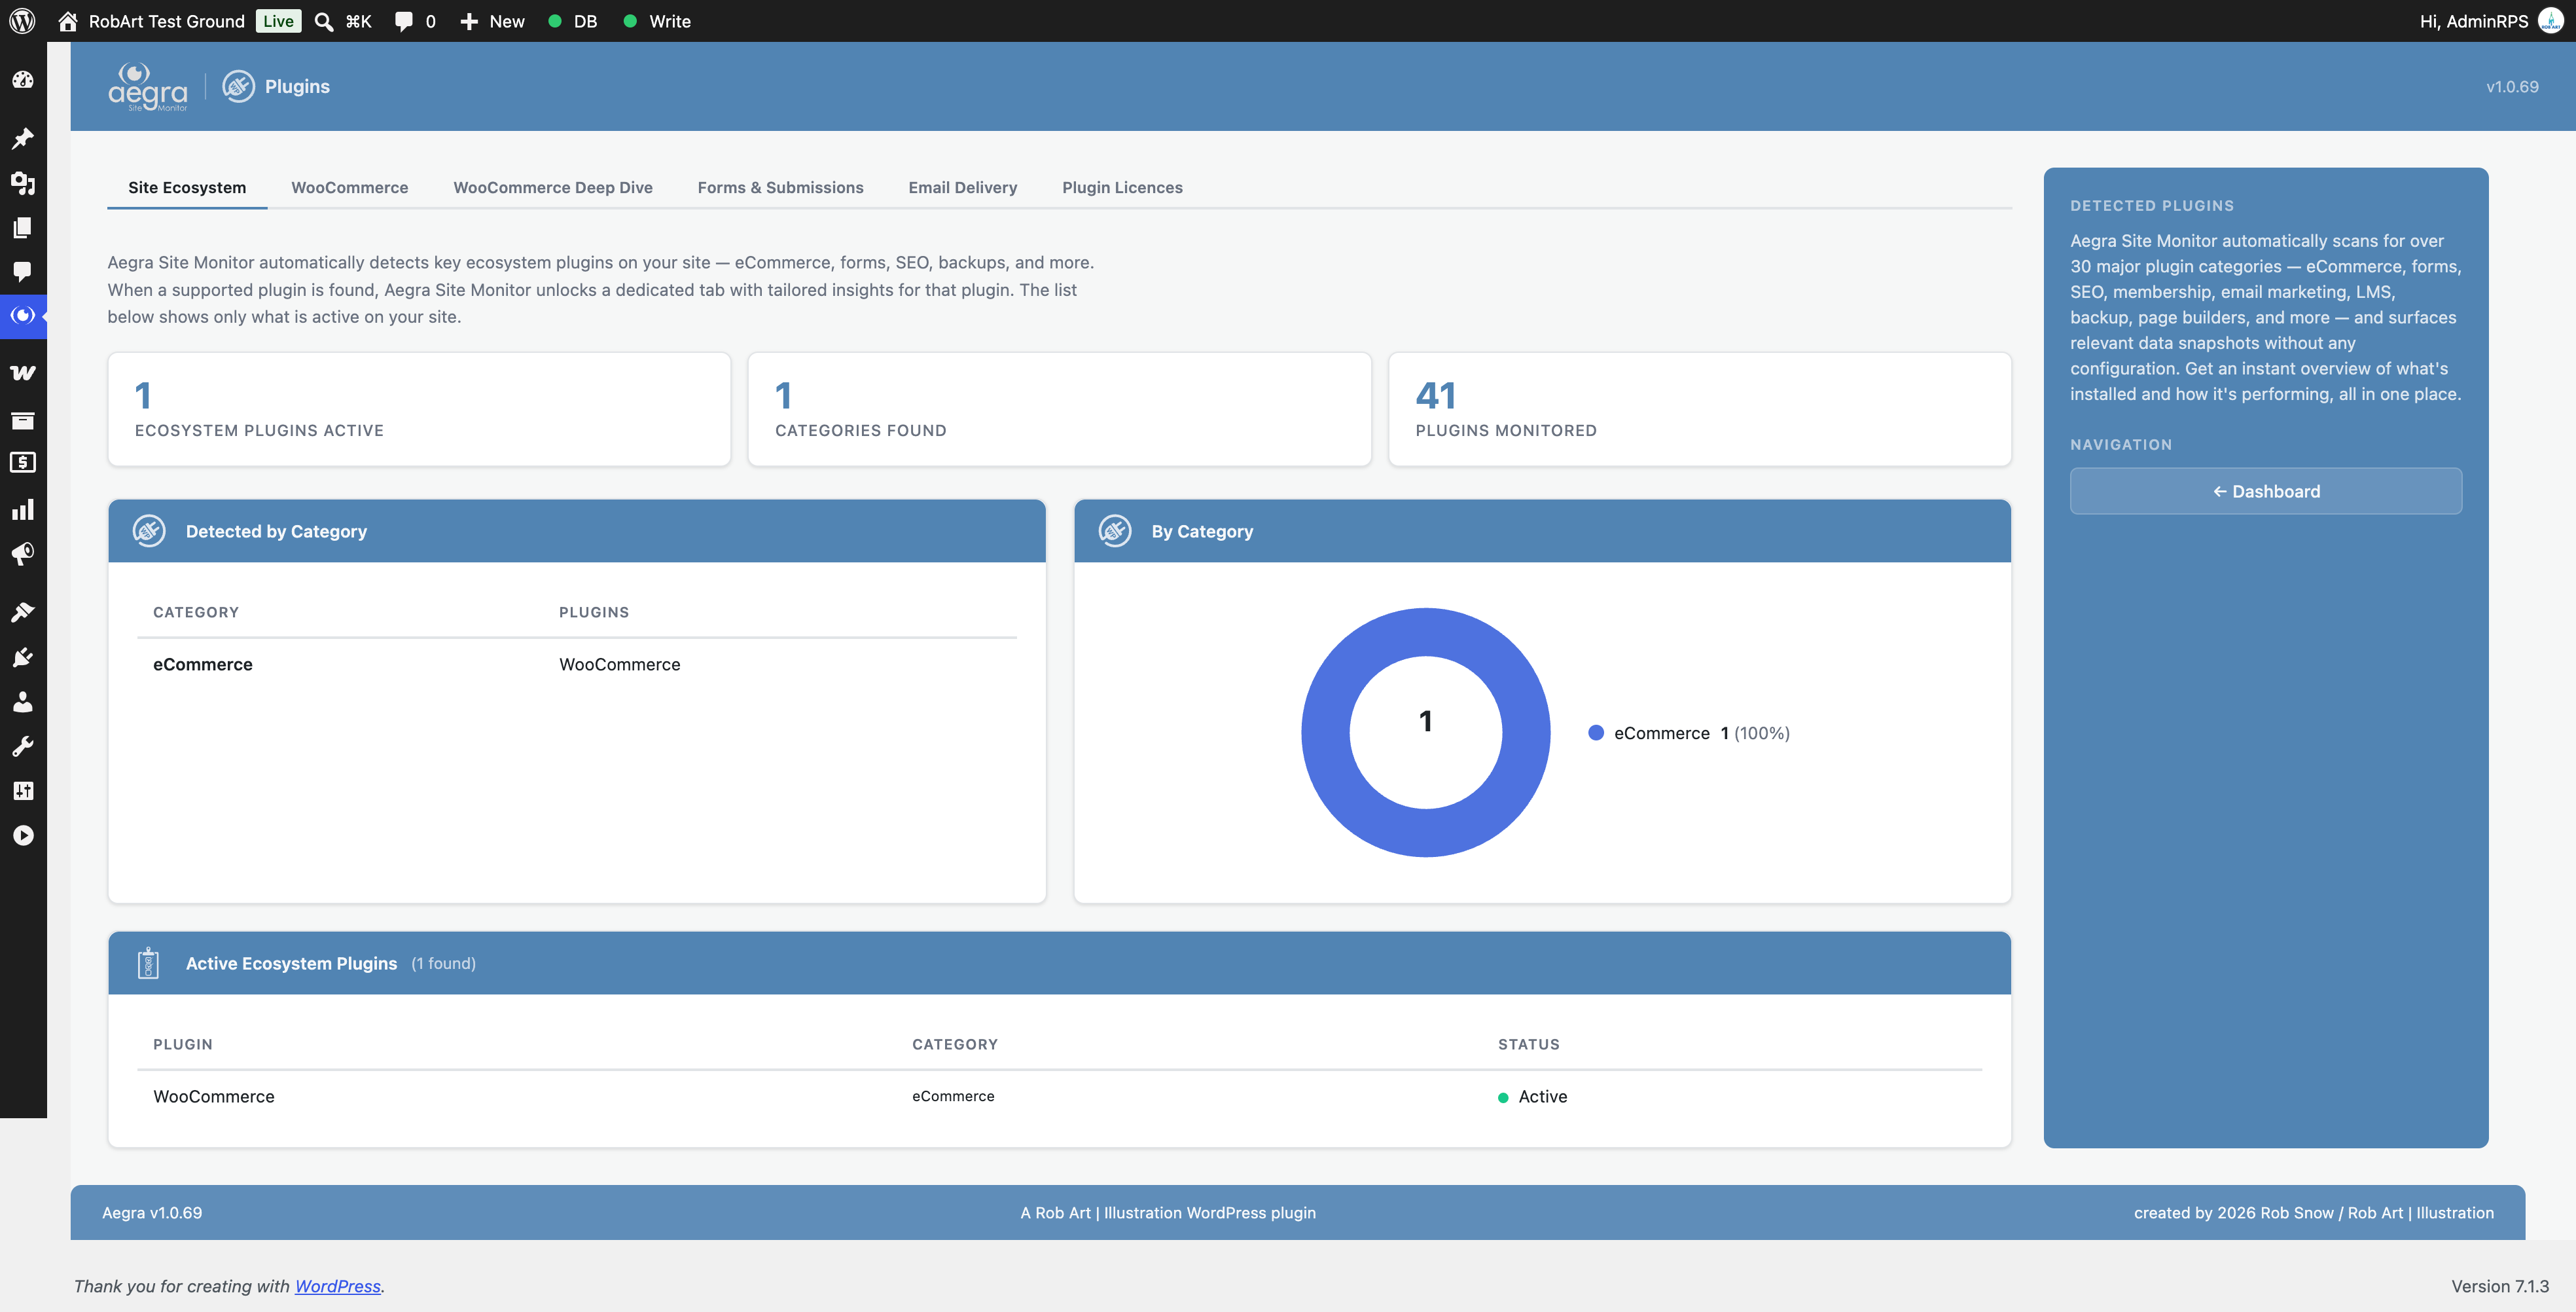
- Changed Plugins tab renamed to Site Ecosystem, redesigned with stat cards and detected-only checklist
- Changed Other Plugins and Bookings plugin snapshots switched to stat cards
- Changed Reports empty-state icons switched to blue versions across all tabs
- Changed Reports > Multisite instruction text updated with direct link to API & Webhooks tab
- Changed Frontend > Revision Bloat Go to Tools button replaced with inline code instructions
- Changed Bar column headers renamed to Relative Size across Media and Performance pages
1.0.1
- Added manual, readme, and licence overlays to dashboard sidebar
- Minor UI refinements
1.0.0
- Initial release